
最新发布第603页

CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
 2025年6月10日 15:02
Jupyter Notebook 未授权访问远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 Jupyter Notebook 未授权访问远程命令执行漏洞 Jupyter Notebook(此前被称为 IPython notebook)是一个交互式笔记本,支持运行 40 多...
2026年2月13日 12:53CVE-2019-20183: Simple Employee Records System 1.0 – Unrestricted File Upload
漏洞标题 CVE-2019-20183: Simple Employee Records System 1.0 - Unrestricted File Upload 漏洞描述 Simple Employee Records System 1.0 contains an arbitrary file upload vulnerability d...
2019年6月1日 08:10CVE-2021-22122: FortiWeb – Cross Site Scripting
漏洞标题 CVE-2021-22122: FortiWeb - Cross Site Scripting 漏洞描述 FortiWeb 6.3.0 through 6.3.7 and versions before 6.2.4 contain an unauthenticated cross-site scripting vulnerabili...
2021年10月17日 12:31CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年9月8日 18:41CVE-2021-24862: WordPress RegistrationMagic <5.0.1.6 - Authenticated SQL Injection
漏洞标题 CVE-2021-24862: WordPress RegistrationMagic <5.0.1.6 - Authenticated SQL Injection 漏洞描述 WordPress RegistrationMagic plugin before 5.0.1.6 contains an authenticated ...
2021年9月1日 09:52CVE-2023-4220: Chamilo LMS <= 1.11.24 - Remote Code Execution
漏洞标题 CVE-2023-4220: Chamilo LMS <= 1.11.24 - Remote Code Execution 漏洞描述 Unrestricted file upload in big file upload functionality in `/main/inc/lib/javascript/bigupload/...
2023年4月17日 07:12Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776)
漏洞标题 Apache Struts2-输入验证漏洞(S2-057)(CVE-2018-11776) 漏洞描述 【漏洞对象】Apache Struts 2 【涉及版本】2.3-2.3.34,2.5-2.5.16 【漏洞描述】软件存在输入验证漏洞,远程攻击者可...
2018年8月31日 07:34CVE-2023-32315-2: Openfire身份认证绕过漏洞
漏洞标题 CVE-2023-32315-2: Openfire身份认证绕过漏洞 漏洞描述 Openfire is an XMPP server licensed under the Open Source Apache License. Openfire's administrative console, a web...
2023年10月22日 10:58CVE-2025-34026: Versa Concerto Actuator Endpoint – Authentication Bypass
漏洞标题 CVE-2025-34026: Versa Concerto Actuator Endpoint - Authentication Bypass 漏洞描述 An authentication bypass vulnerability affected the Spring Boot Actuator endpoints in Ver...
2025年8月23日 11:28CVE-2019-3398: Atlassian Confluence Download Attachments – Remote Code Execution
漏洞标题 CVE-2019-3398: Atlassian Confluence Download Attachments - Remote Code Execution 漏洞描述 Confluence Server and Data Center had a path traversal vulnerability in the downl...
2019年12月22日 07:56CVE-2023-41266: Qlik Sense Enterprise – Path Traversal
漏洞标题 CVE-2023-41266: Qlik Sense Enterprise - Path Traversal 漏洞描述 A path traversal vulnerability found in Qlik Sense Enterprise for Windows for versions May 2023 Patch 3 and...
2023年12月12日 23:43CVE-2021-41460: ECShop 4.1.0 – SQL Injection
漏洞标题 CVE-2021-41460: ECShop 4.1.0 - SQL Injection 漏洞描述 ECShop 4.1.0 has SQL injection vulnerability, which can be exploited by attackers to obtain sensitive information. Po...
2021年7月23日 06:59CVE-2020-8772: WordPress InfiniteWP <1.9.4.5 - Authorization Bypass
漏洞标题 CVE-2020-8772: WordPress InfiniteWP <1.9.4.5 - Authorization Bypass 漏洞描述 WordPress InfiniteWP plugin before 1.9.4.5 for WordPress contains an authorization bypass v...
2020年10月5日 07:40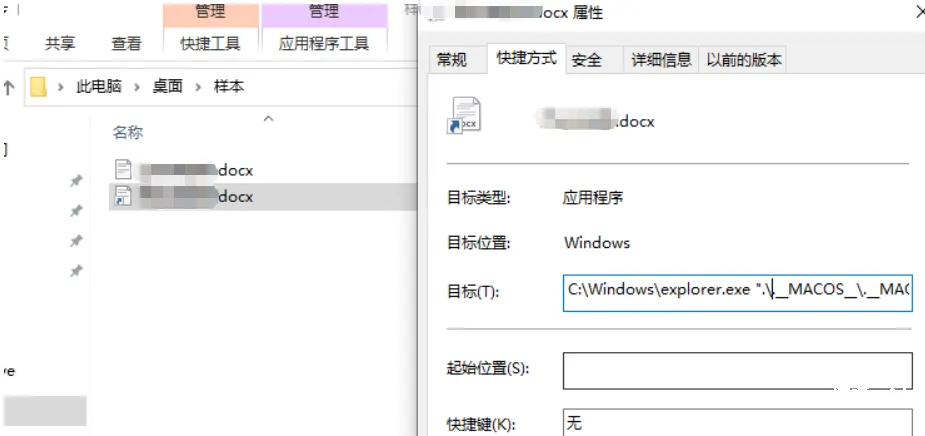
某攻防钓鱼样本分析
https://xz.aliyun.com/news/91931 基础静态分析 拿到样本解压目录看只有lnk和一个Word文档,基本确定为LNK钓鱼马了,看下lnk执行的命令:如下图 打开查看目录结构发现LNK执行命令指向exe,查看...

 2026年4月24日 16:31
CVE-2024-54767: AVM FRITZ!Box 7530 AX – Unauthorized Access
漏洞标题 CVE-2024-54767: AVM FRITZ!Box 7530 AX - Unauthorized Access 漏洞描述 An access control issue in the component /juis_boxinfo.xml of AVM FRITZ!Box 7530 AX v7.59 allows attac...
2024年3月14日 05:25
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

