
最新发布第707页

CVE-2018-14912: cgit < 1.2.1 - Directory Traversal
漏洞标题 CVE-2018-14912: cgit < 1.2.1 - Directory Traversal 漏洞描述 cGit < 1.2.1 via cgit_clone_objects has a directory traversal vulnerability when `enable-http-clone=1` is...
 2018年1月14日 04:33
CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure
漏洞标题 CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure 漏洞描述 WordPress WPS Hide Login plugin before 1.9.1 is susceptible to incorrect authorization...
2021年12月10日 07:42Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195)
漏洞标题 Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195) 漏洞描述 Apache OFBiz是一个开源企业资源规划(ERP)系统。它提供了一套企业应用程序,集成并自动化企业的许多业务流程...
2024年12月3日 16:24CVE-2023-29357: Microsoft SharePoint – Authentication Bypass
漏洞标题 CVE-2023-29357: Microsoft SharePoint - Authentication Bypass 漏洞描述 Microsoft SharePoint Server Elevation of Privilege Vulnerability PoC代码
2023年3月3日 05:54
bugbounty技巧聚合20210818
漏洞报告 MTN Grou #1060518 No rate limit in otp code sending Mail.ru #1255676 Blind XSS Stored and CORS misconfiguration в отчете 'События' сервиса top.mail.ru...
2022年3月10日 23:32
越权tips之某src猜测接口,找到越权漏洞
打开xxx.com,f12翻js文件, 里面一堆接口,但只有查找menu列表的接口可以访问,http://xxx.com/api/v1/menu/list js文件中没有添加和删除menu信息的接口,但是之前搞过类似的,这里就想着构造...
2022年3月10日 23:35CVE-2024-12209: WP Umbrella Update Backup Restore & Monitoring <= 2.17.0 - Local File Inclusion
漏洞标题 CVE-2024-12209: WP Umbrella Update Backup Restore & Monitoring <= 2.17.0 - Local File Inclusion 漏洞描述 The WP Umbrella: Update Backup Restore & Monitoring plu...
2024年10月13日 15:15CVE-2010-3867: ProFTPD < 1.3.3c - Directory Traversal via mod_site_misc
漏洞标题 CVE-2010-3867: ProFTPD < 1.3.3c - Directory Traversal via mod_site_misc 漏洞描述 ProFTPD versions before 1.3.3c contain directory traversal vulnerabilities in the mod_s...
2010年2月4日 06:01CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年12月23日 11:58CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation
漏洞标题 CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation 漏洞描述 An Improper Access Control vulnerability...
2021年12月17日 06:57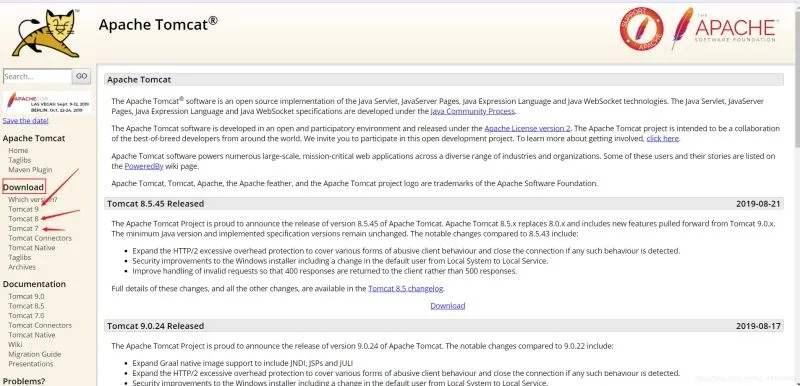
Tomcat下载安装并部署到IDEA的教程(附带idea两种热部署设置方法)_Tomcat
这篇文章主要介绍了Tomcat下载安装并部署到IDEA的教程(附带idea两种热部署设置方法),本文图文并茂给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 目录Tomcat下载教程To...
2026年4月6日 11:45CVE-2022-30489: Wavlink WN-535G3 – Cross-Site Scripting
漏洞标题 CVE-2022-30489: Wavlink WN-535G3 - Cross-Site Scripting 漏洞描述 Wavlink WN-535G3 contains a POST cross-site scripting vulnerability via the hostname parameter at /cgi-bin...
2022年12月3日 22:12CVE-2021-41277 Metabase 信息泄露漏洞
漏洞标题 CVE-2021-41277 Metabase 信息泄露漏洞 漏洞描述 CVE-2021-41277 Metabase 信息泄露漏洞 PoC代码 暂无
2021年1月8日 12:44CVE-2021-25111: WordPress English Admin <1.5.2 - Open Redirect
漏洞标题 CVE-2021-25111: WordPress English Admin <1.5.2 - Open Redirect 漏洞描述 WordPress English Admin plugin before 1.5.2 contains an open redirect vulnerability. The plugin ...
2021年9月15日 01:00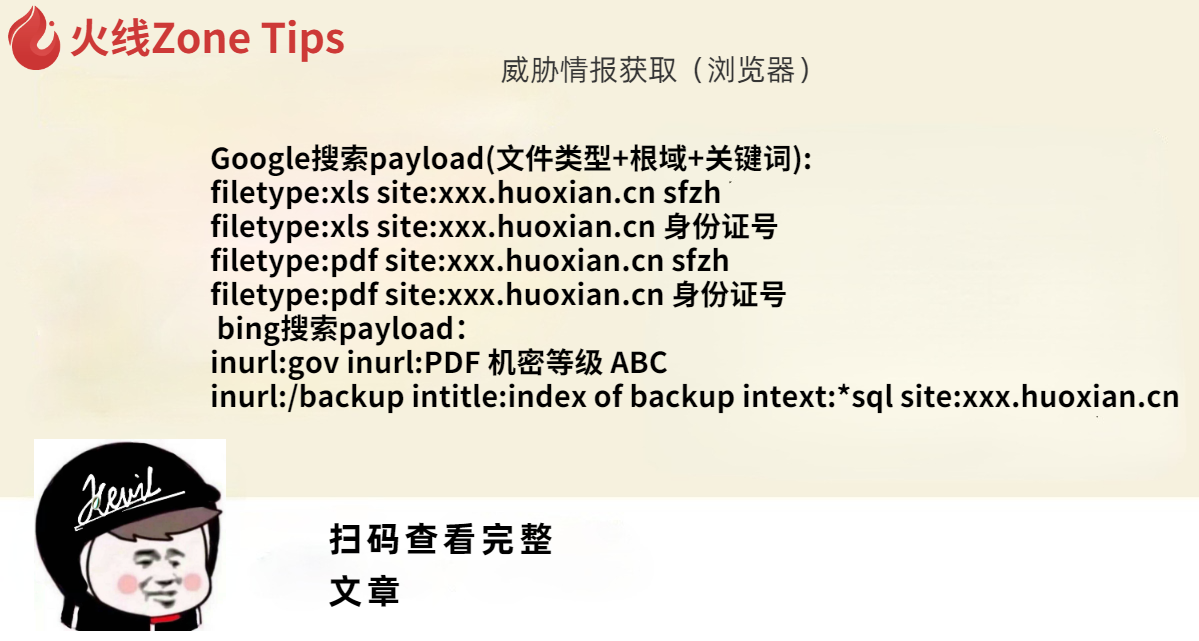
威胁情报获取(浏览器)
Google搜索payload(文件类型+根域+关键词): filetype:xls site:xxx.huoxian.cn sfzh filetype:xls site:xxx.huoxian.cn 身份证号 filetype:pdf site:xxx.huoxian.cn sfzh filetype:pdf site:xxx...
2022年3月10日 23:34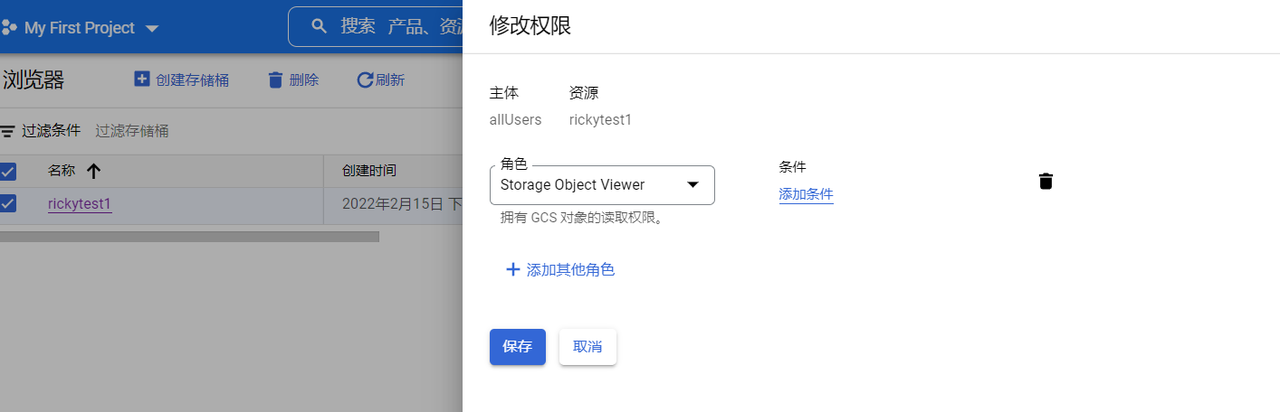
谷歌云 对象存储攻防
本文主要介绍谷歌云对象存储攻防的方式 1、存储桶配置错误-公开访问 当创建的存储桶配置了allUsers拥有GCS对象的读取权限时,该存储桶可以被任何用户公开访问 2、Bucket爆破 当不存在时访问会提...
2022年3月10日 23:38
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

