
最新发布第731页

CVE-2010-1471: Joomla! Component Address Book 1.5.0 – Local File Inclusion
漏洞标题 CVE-2010-1471: Joomla! Component Address Book 1.5.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the AddressBook (com_addressbook) component 1.5....
 2010年11月26日 05:07
CVE-2022-24706: CouchDB Erlang Distribution – Remote Command Execution
漏洞标题 CVE-2022-24706: CouchDB Erlang Distribution - Remote Command Execution 漏洞描述 In Apache CouchDB prior to 3.2.2, an attacker can access an improperly secured default inst...
2022年3月20日 07:08CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass
漏洞标题 CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass 漏洞描述 The MStore API plugin for WordPress is vulnerable to authentication bypass in versions up to, and in...
2023年2月16日 08:50
什么是 IP 冲突以及如何解决?
如果你曾经看到“Windows 检测到 IP 地址冲突”或“此网络上的另一台计算机具有相同的 IP 地址”消息,你可能想知道此警告的含义。虽然 IP 冲突问题通常不难解决,但它们令人困惑,尤其是对于那...
2022年5月7日 18:11CVE-2025-32814: NetMRI Unauthenticated SQL Injection via skipjackUsername
漏洞标题 CVE-2025-32814: NetMRI Unauthenticated SQL Injection via skipjackUsername 漏洞描述 An issue was discovered in Infoblox NETMRI before 7.6.1. Unauthenticated SQL Injection c...
2025年8月2日 01:39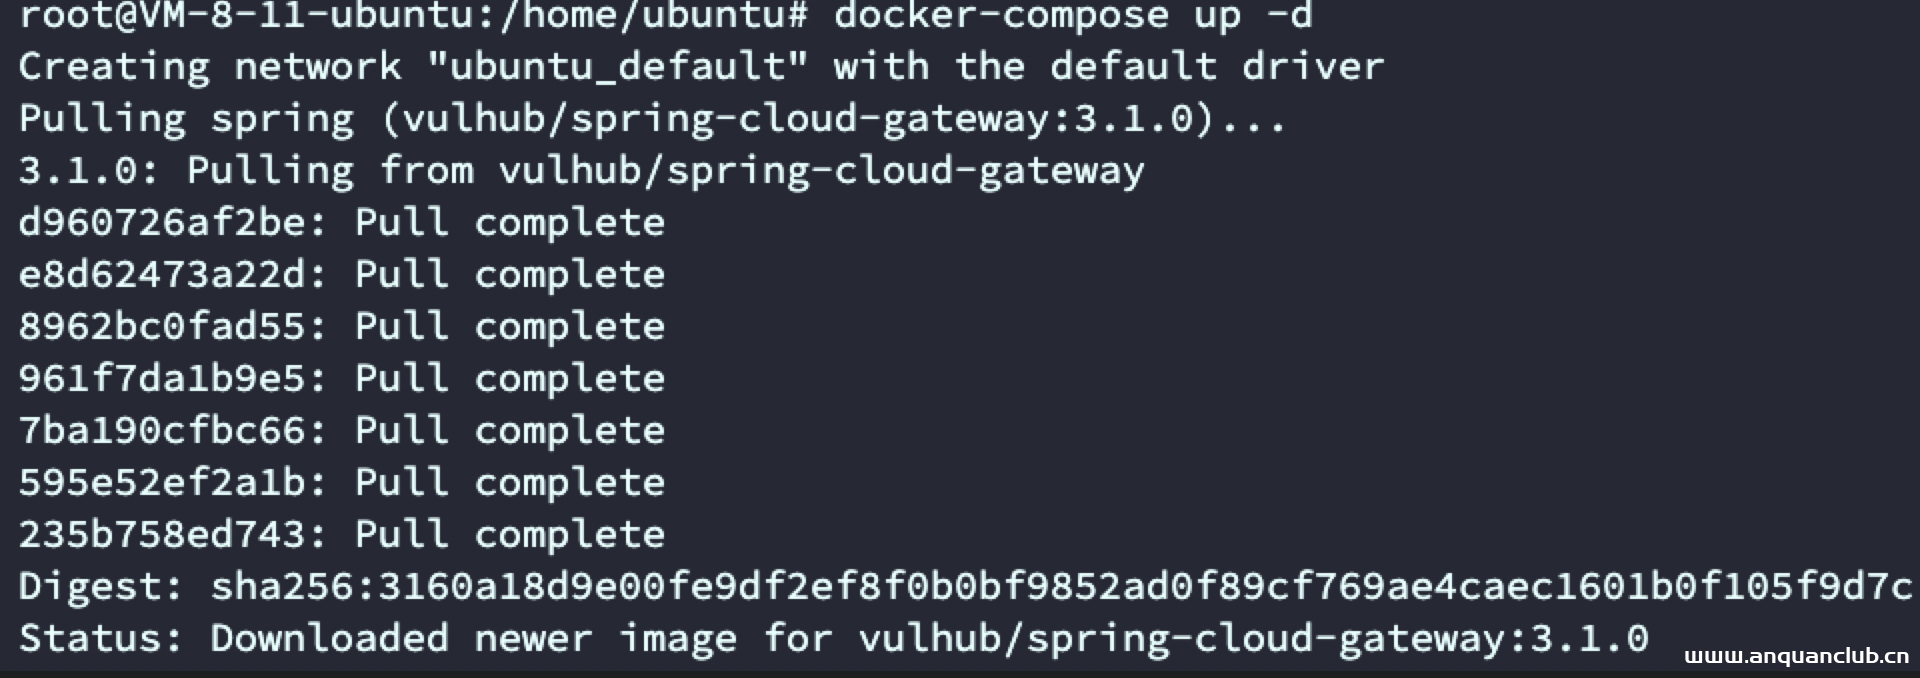
Spring_Cloud_Gateway_Actuator_API_SpEL表达式注入命令执行(CVE-2022-22947)
虽然现在发有点像炒冷饭?不过前几天太忙了 没时间看 既然复现了就记录一下吧 一、环境搭建 http://github.com/vulhub/vulhub/tree/master/spring/CVE-2022-22947 docker-compose up -d 二、漏...
2022年3月10日 23:39CVE-2017-14725: WordPress < 4.8.2 - Authenticated Open Redirect
漏洞标题 CVE-2017-14725: WordPress < 4.8.2 - Authenticated Open Redirect 漏洞描述 WordPress versions before 4.8.2 contain an open redirect caused by improper validation in wp-ad...
2017年1月28日 03:56CVE-2017-8046: Spring Data Rest RCE
漏洞标题 CVE-2017-8046: Spring Data Rest RCE 漏洞描述 SpringDataREST是一个构建在SpringData之上,为了帮助开发者更加容易地开发REST风格的Web服务。在RESTAPI的Patch方法中(实现RFC6902)...
2017年5月9日 16:27
致远OA htmlofficeservlet 任意文件上传
本文转载于公众号:融云攻防实验室,原文地址: 致远OA htmlofficeservlet 任意文件上传 致远OA办公自动化软件,用于OA办公自动化软件的开发销售。2010年,用友致远更名为致远协创。2017年更名...
2026年2月13日 12:53CVE-2025-61757: Oracle Identity Manager REST WebServices – Authentication Bypass
漏洞标题 CVE-2025-61757: Oracle Identity Manager REST WebServices - Authentication Bypass 漏洞描述 Vulnerability in the Identity Manager product of Oracle Fusion Middleware (compon...
2025年9月8日 05:17CVE-2024-33610: Sharp Multifunction Printers – Cookie Exposure
漏洞标题 CVE-2024-33610: Sharp Multifunction Printers - Cookie Exposure 漏洞描述 It was observed that Sharp printers are vulnerable to a listing of session cookies without authenti...
2024年12月4日 02:37CVE-2024-40711: Veeam Backup & Replication – Unauthenticated
漏洞标题 CVE-2024-40711: Veeam Backup & Replication - Unauthenticated 漏洞描述 A deserialization of untrusted data vulnerability with a malicious payload can allow an unauthent...
2024年10月5日 02:51CVE-2024-41107: Apache CloudStack – SAML Signature Exclusion
漏洞标题 CVE-2024-41107: Apache CloudStack - SAML Signature Exclusion 漏洞描述 The CloudStack SAML authentication (disabled by default) does not enforce signature check. In CloudSt...
2024年9月7日 13:18CVE-2020-8209: Citrix XenMobile Server – Local File Inclusion
漏洞标题 CVE-2020-8209: Citrix XenMobile Server - Local File Inclusion 漏洞描述 Citrix XenMobile Server 10.12 before RP2, Citrix XenMobile Server 10.11 before RP4, Citrix XenMobile...
2020年10月4日 06:35CVE-2010-1345: Joomla! Component Cookex Agency CKForms – Local File Inclusion
漏洞标题 CVE-2010-1345: Joomla! Component Cookex Agency CKForms - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Cookex Agency CKForms (com_ckforms) compo...
2010年9月19日 19:08Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
2023年3月3日 16:26
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

