
最新发布第77页

CVE-2022-23134: Zabbix Setup Configuration Authentication Bypass
漏洞标题 CVE-2022-23134: Zabbix Setup Configuration Authentication Bypass 漏洞描述 After the initial setup process, some steps of setup.php file are reachable not only by super-adm...
 2022年7月8日 12:27
CVE-2021-26072: Atlassian Confluence < 5.8.6 - Server-Side Request Forgery
漏洞标题 CVE-2021-26072: Atlassian Confluence < 5.8.6 - Server-Side Request Forgery 漏洞描述 Confluence Server and Data Center before 5.8.6 contain a blind server-side request f...
2021年5月13日 01:41CVE-2024-9047: WordPress File Upload <= 4.24.11 - Arbitrary File Read
漏洞标题 CVE-2024-9047: WordPress File Upload <= 4.24.11 - Arbitrary File Read 漏洞描述 The WordPress File Upload plugin for WordPress is vulnerable to Path Traversal in all ver...
2024年11月29日 16:05CVE-2019-10717: BlogEngine.NET 3.3.7.0 – Local File Inclusion
漏洞标题 CVE-2019-10717: BlogEngine.NET 3.3.7.0 - Local File Inclusion 漏洞描述 BlogEngine.NET 3.3.7.0 allows /api/filemanager local file inclusion via the path parameter PoC代码
2019年1月13日 07:52CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
2012年6月26日 06:25CVE-2023-22629: TitanFTP move-file Function ≤ 1.94.1205 – Path Traversal
漏洞标题 CVE-2023-22629: TitanFTP move-file Function ≤ 1.94.1205 - Path Traversal 漏洞描述 TitanFTP versions up to 1.94.1205 contain a path traversal vulnerability in the move-fil...
2023年5月11日 22:03CVE-2019-12988: Citrix SD-WAN Center – Remote Command Injection
漏洞标题 CVE-2019-12988: Citrix SD-WAN Center - Remote Command Injection 漏洞描述 Citrix SD-WAN Center is susceptible to remote command injection via the addModifyZTDProxy function...
2019年5月16日 17:19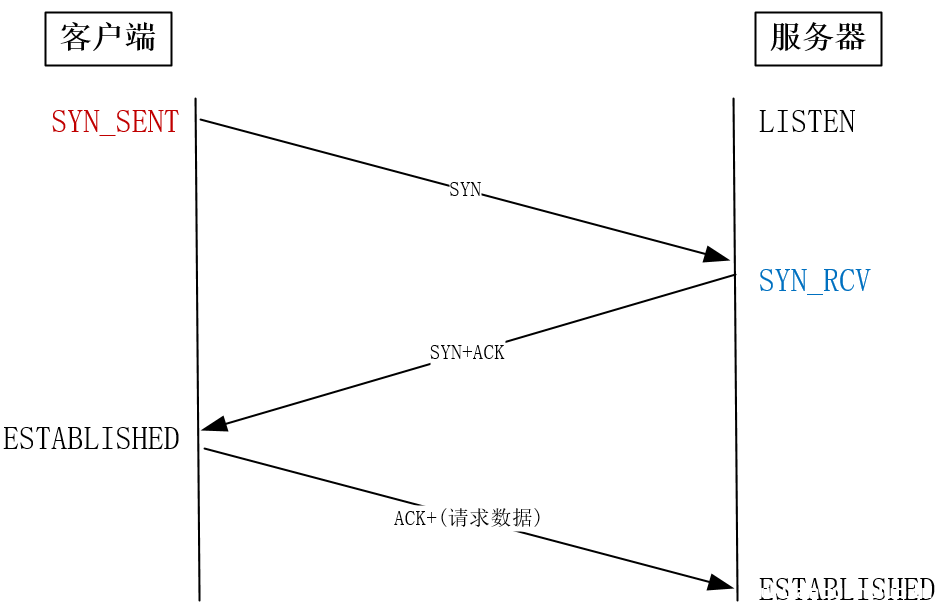
TCP性能调优实现原理及过程解析_服务器其它
这篇文章主要介绍了TCP性能调优实现原理及过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 三次握手阶段 客户端SYN包的重试次数 s...
2023年1月10日 21:40CVE-2020-28187: TerraMaster TOS 后台任意文件读取漏洞
漏洞标题 CVE-2020-28187: TerraMaster TOS 后台任意文件读取漏洞 漏洞描述 TerraMaster TOS <= 4.2.06中的多个目录遍历漏洞允许远程身份验证的攻击者通过/tos/index.php?editor/fileGet路径...
2020年5月10日 20:24CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059
漏洞标题 CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059 漏洞描述 Apache Struts 2.0.0 to 2.5.20 forced double OGNL evaluation when evaluated on raw user inp...
2019年11月9日 08:47confluence 远程代码执行漏洞(CVE-2019-3396)
漏洞标题 confluence 远程代码执行漏洞(CVE-2019-3396) 漏洞描述 Confluence是一个专业的企业知识管理与协同软件,常用于构建企业wiki。它强大的编辑和站点管理特征能够帮助团队成员之间共享信...
2019年5月16日 02:47
解决Linux+Apache服务器URL区分大小写问题_Linux
Linux服务器的大小写敏感有时候很不方便,在地址栏里一定要输入准确的URL才能访问,对搜索引擎和用户不是很友好,那么如何解决LINUX服务器URL的大小写问题 今天同步碰到一个问题,在浏览器地址...
2024年6月13日 21:06CVE-2023-3848: MooDating 1.2 – Cross-site scripting
漏洞标题 CVE-2023-3848: MooDating 1.2 - Cross-site scripting 漏洞描述 A vulnerability, which was classified as problematic, has been found in mooSocial mooDating 1.2. This issue af...
2023年2月10日 14:10CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure
漏洞标题 CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure 漏洞描述 The Trinity Audio Text to Speech AI audio player to convert content into audio plugin for WordPre...
2025年8月20日 05:07CVE-2017-8229: Amcrest IP Camera Web Management – Data Exposure
漏洞标题 CVE-2017-8229: Amcrest IP Camera Web Management - Data Exposure 漏洞描述 Amcrest IPM-721S V2.420.AC00.16.R.20160909 devices allow an unauthenticated attacker to download t...
2017年1月11日 08:58CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read
漏洞标题 CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read 漏洞描述 Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser t...
2024年12月13日 20:14
2026年11月2日 11:45
2026年11月2日 11:45
2026年11月1日 11:45
2026年10月31日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

