
最新发布第789页
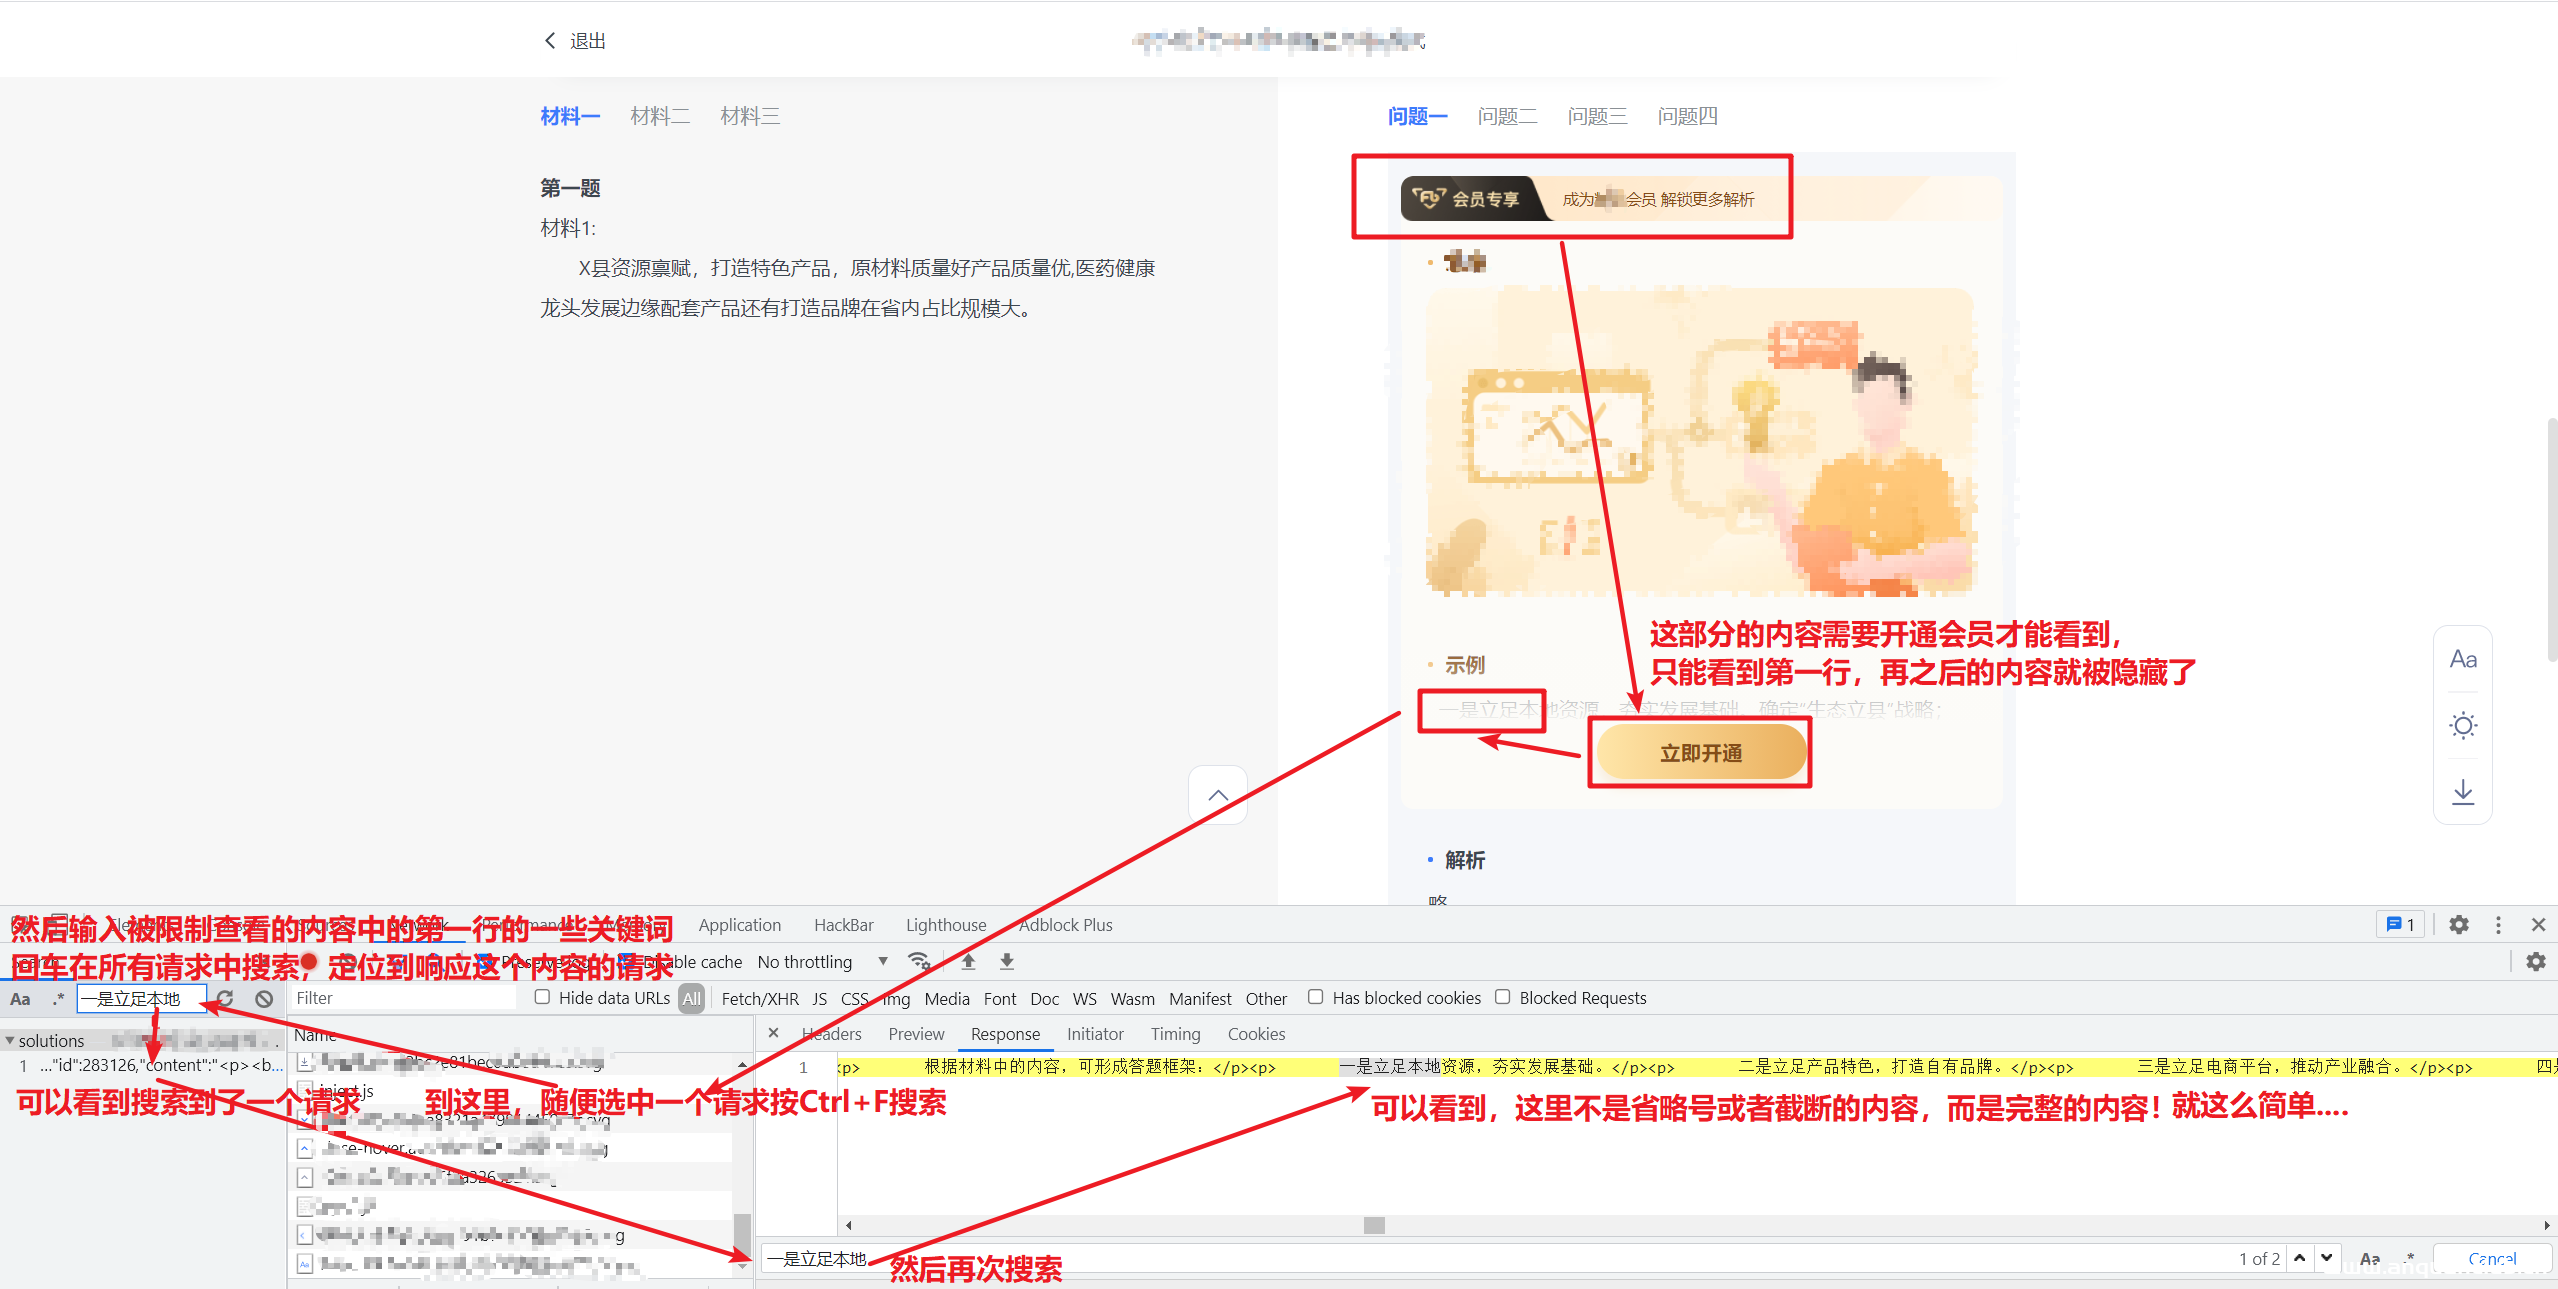
水一发:vip业务权限漏洞挖掘入门姿势实战
现在很多网站都是通过卖VIP会员盈利的,为了让用户更有购买欲望,有的时候会把内容展示一小部分,然后隐藏绝大多部分,让你看完一点还想看就忍不住付钱了:),产品经理的愿景是很美好的,但是...
 2022年3月10日 23:33

CVE-2025-2264: Sante PACS Server.exe – Path Traversal Information Disclosure
漏洞标题 CVE-2025-2264: Sante PACS Server.exe - Path Traversal Information Disclosure 漏洞描述 A Path Traversal Information Disclosure vulnerability exists in "Sante PACS Serv...
2025年7月11日 13:33
详解复制备份docker容器数据的方法_docker
这篇文章主要介绍了详解复制备份docker容器数据的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 这里以jenki...
2024年2月27日 21:29CVE-2025-2747: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0006)
漏洞标题 CVE-2025-2747: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0006) 漏洞描述 An authentication bypass vulnerability in Kentico Xperience allows ...
2025年7月6日 05:21Linux下Jenkins忘记密码的操作步骤_Linux
这篇文章主要介绍了Linux下Jenkins忘记密码的操作步骤,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 1.Jenkins安装步骤: http://www.jb51.net/article/176615.htm...
2026年3月15日 11:45CVE-2024-24329: TotoLink Router setPortForwardRules – Command Injection
漏洞标题 CVE-2024-24329: TotoLink Router setPortForwardRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vuln...
2024年9月3日 14:53CVE-2024-11396: Event Monster <= 1.4.3 - Information Exposure Via Visitors List Export
漏洞标题 CVE-2024-11396: Event Monster <= 1.4.3 - Information Exposure Via Visitors List Export 漏洞描述 The Event Monster Event Management, Tickets Booking, Upcoming Event plug...
2024年3月8日 01:29CVE-2020-28351: Mitel ShoreTel 19.46.1802.0 Devices – Cross-Site Scripting
漏洞标题 CVE-2020-28351: Mitel ShoreTel 19.46.1802.0 Devices - Cross-Site Scripting 漏洞描述 Mitel ShoreTel 19.46.1802.0 devices and their conference component are vulnerable to an...
2020年7月14日 04:18CVE-2023-39024: Harman Media Suite <= 4.2.0 - Local File Disclosure
漏洞标题 CVE-2023-39024: Harman Media Suite <= 4.2.0 - Local File Disclosure 漏洞描述 Harman Media Suite (versions 4.2.0 and below) are vulnerable to possible Local File Disclos...
2023年12月5日 06:38CVE-2024-38653: Ivanti Avalanche SmartDeviceServer – XML External Entity
漏洞标题 CVE-2024-38653: Ivanti Avalanche SmartDeviceServer - XML External Entity 漏洞描述 XXE in SmartDeviceServer in Ivanti Avalanche 6.3.1 allows a remote unauthenticated attack...
2024年8月15日 06:05
【防骗科普】菠菜网站是如何一步一步让你深陷泥潭,直到倾家荡产
论菠菜网站是如何一步一步让你深陷泥潭,直到倾家荡产的,今天借助一个同学分享的违规站点进行讲解,虽然该站点没有用户使用,但是远离赌博,人人有责! 第一部分 首先清楚今天的主角 因为主页...

 2023年1月13日 19:50
CVE-2020-7107: WordPress Ultimate FAQ <1.8.30 - Cross-Site Scripting
漏洞标题 CVE-2020-7107: WordPress Ultimate FAQ <1.8.30 - Cross-Site Scripting 漏洞描述 WordPress Ultimate FAQ plugin before 1.8.30 is susceptible to cross-site scripting via Dis...
2020年12月1日 00:10CVE-2021-29156: LDAP Injection In OpenAM
漏洞标题 CVE-2021-29156: LDAP Injection In OpenAM 漏洞描述 OpenAM contains an LDAP injection vulnerability. When a user tries to reset his password, they are asked to enter usernam...
2021年9月18日 22:18CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload
漏洞标题 CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload 漏洞描述 The Migration, Backup, Staging – WPvivid Backu...
2025年2月8日 12:41CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion
漏洞标题 CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion 漏洞描述 WordPress MyPixs 0.3 and prior contains a local file inclusion vulnerability. PoC代码
2015年1月23日 08:59CVE-2021-31195: Microsoft Exchange Server – Cross-Site Scripting
漏洞标题 CVE-2021-31195: Microsoft Exchange Server - Cross-Site Scripting 漏洞描述 Microsoft Exchange Server, or OWA, is vulnerable to a cross-site scripting vulnerability in refur...
2021年8月28日 12:19
2026年11月16日 11:45
2026年11月15日 11:45
2026年11月14日 11:45
2026年11月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

