
最新发布第795页

CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
 2023年4月3日 01:27
CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass
漏洞标题 CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass 漏洞描述 Hard-Coded Cryptographic key allowing to forge session cookies that can be used to ent...
2025年2月7日 10:18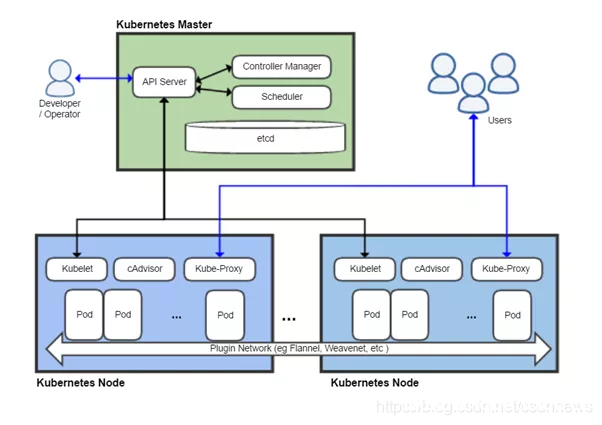
被弃用的 Docker 会被 Podman 取代吗_docker
Docker 是一种以容器化的方式打包、分发和部署应用程序的方式。自 2013 年 3 月 13 日初始版本发布以来,Docker 已成为容器业界的事实标准。而Kubernetes 是一款由 Google 开发的开源容器编排系...
2022年11月23日 20:07CVE-2018-11133: Quest KACE SMA /common/run_cross_report.php ‘fmt’ XSS
漏洞标题 CVE-2018-11133: Quest KACE SMA /common/run_cross_report.php 'fmt' XSS 漏洞描述 The 'fmt' parameter of the '/common/run_cross_report.php' scri...
2018年6月30日 23:35CVE-2010-1217: Joomla! Component & Plugin JE Tooltip 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1217: Joomla! Component & Plugin JE Tooltip 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the JE Form Creator (com_jeformcr) comp...
2010年8月30日 17:26CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS
漏洞标题 CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS 漏洞描述 FileZilla Server versions prior to 0.9.31 contain a buffer overflow vulnerability relate...
2009年4月5日 05:19AtMail 6.5.0反射型XSS漏洞(CVE-2022-30776)
漏洞标题 AtMail 6.5.0反射型XSS漏洞(CVE-2022-30776) 漏洞描述 AtMail是一个开源的WebMail客户端。它提供“清爽”的Ajax Webmail界面,支持通信录管理,并且支持IMAP。AtMail存在过滤不完全的...
2022年7月4日 21:10CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection
漏洞标题 CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection 漏洞描述 The plugin does not sanitise and escape some parameter before using it in a SQL statement via ...
2022年4月5日 04:40CVE-2022-2863: WordPress WPvivid Backup <0.9.76 - Local File Inclusion
漏洞标题 CVE-2022-2863: WordPress WPvivid Backup <0.9.76 - Local File Inclusion 漏洞描述 WordPress WPvivid Backup version 0.9.76 is vulnerable to local file inclusion because th...
2022年3月21日 01:52CVE-2024-11303: Korenix JetPort 5601v3 – Path Traversal
漏洞标题 CVE-2024-11303: Korenix JetPort 5601v3 - Path Traversal 漏洞描述 The pathname of the root directory to a Restricted Directory ('Path Traversal') vulnerability in...
2024年6月24日 07:38
bugbounty技巧聚合20220126
漏洞报告 【Imgur】密码无长度 http://hackerone.com/reports/1411363 【Mail.ru 】子域接管 http://hackerone.com/reports/1348504 【Lark Technologies】能够使用 Lark 的 Compose Email 功能...
2022年3月10日 23:39CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 – Remote Code Execution
漏洞标题 CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 - Remote Code Execution 漏洞描述 Sunlogin Sunflower Simplified (aka Sunflower Simple and Personal) 1.0.1.43315 is...
2022年4月10日 23:44CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection
漏洞标题 CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection 漏洞描述 The HTML5 Video Player WordPress plugin before 2.5.27 does not sanitize and escape a param...
2024年10月2日 13:27CVE-2022-1950: WordPress Youzify sql injection
漏洞标题 CVE-2022-1950: Wordpress Youzify sql injection 漏洞描述 The Youzify WordPress plugin before 1.2.0 does not sanitise and escape a parameter before using it in a SQL stateme...
2022年6月7日 01:55CVE-2021-29203: HPE Edgeline Infrastructure Manager <1.22 - Authentication Bypass
漏洞标题 CVE-2021-29203: HPE Edgeline Infrastructure Manager <1.22 - Authentication Bypass 漏洞描述 HPE Edgeline Infrastructure Manager, also known as HPE Edgeline Infrastructur...
2021年9月2日 23:44
clash最新RCE复现
杂谈 Clash相信你们都不陌生,就是我们平常使用VPN时最常用的软件 先前就曾出现过rce漏洞,现在有爆出了,可以参考以前的文章 软件版本 0.20.12 操作系统 Windows x64 系统版本 Windows 11 问题...

 2023年1月15日 13:49

2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

