
最新发布第813页

CVE-2020-11441: phpMyAdmin 5.0.2 – CRLF Injection
漏洞标题 CVE-2020-11441: phpMyAdmin 5.0.2 - CRLF Injection 漏洞描述 phpMyAdmin 5.0.2 allows CRLF injection, as demonstrated by %0D%0Astring%0D%0A inputs to login form fields causin...
 2020年2月14日 12:53
CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting
漏洞标题 CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting 漏洞描述 The Easy Forms for Mailchimp plugin before version 6.8.9 contains a ref...
2023年2月11日 13:46CVE-2023-38950: ZKTeco BioTime v8.5.5 – Path Traversal
漏洞标题 CVE-2023-38950: ZKTeco BioTime v8.5.5 - Path Traversal 漏洞描述 A path traversal vulnerability in the iclock API of ZKTeco BioTime v8.5.5 allows unauthenticated attackers ...
2023年7月13日 06:42CVE-2021-24498: WordPress Calendar Event Multi View <1.4.01 - Cross-Site Scripting
漏洞标题 CVE-2021-24498: WordPress Calendar Event Multi View <1.4.01 - Cross-Site Scripting 漏洞描述 WordPress Calendar Event Multi View plugin before 1.4.01 contains an unauthe...
2021年4月26日 21:22CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery
漏洞标题 CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery 漏洞描述 WordPress PhonePe Payment Solutions plugin through 1.0.15 is suscept...
2022年11月29日 18:28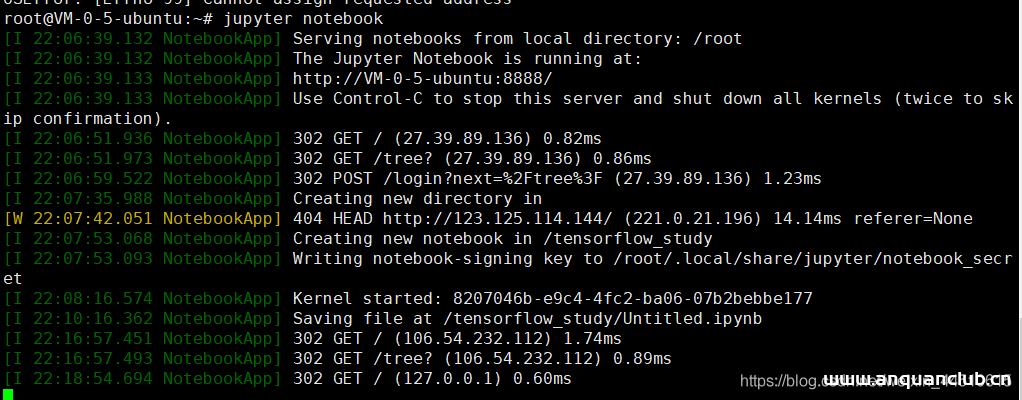
解决服务器运行jupyter notebook方法_服务器其它
这篇文章主要介绍了解决服务器运行jupyter notebook方法,来帮助大家实现服务器跑Jupyter,附含图文以及详细代码,有需要的朋友可以借鉴参考下 目录服务器运行jupyter notebook虚拟环境然后关防...
2022年6月15日 08:54Crestron Devices CVE-2022-23178信息泄露漏洞
漏洞标题 Crestron Devices CVE-2022-23178信息泄露漏洞 漏洞描述 Crestron Devices CVE-2022-23178信息泄露漏洞 日期: 2024-02-22 | 影响软件: Crestron Devices | PoC代码 暂无
2022年5月17日 07:42CVE-2021-22205: GitLab CE/EE – Remote Code Execution
漏洞标题 CVE-2021-22205: GitLab CE/EE - Remote Code Execution 漏洞描述 GitLab CE/EE starting from 11.9 does not properly validate image files that were passed to a file parser, res...
2021年5月7日 11:11
深入浅析Centos 7系统的Tomcat服务器_Tomcat
tomcat最初是由Sun的软件架构师詹姆斯 邓肯 戴维森开发的。后来他帮助将其变为开源项目,并由Sun贡献给Apache软件基金会。这篇文章主要介绍了Centos 7系统的Tomcat服务器的相关知识,需要的朋友...
2026年5月15日 11:45CVE-2017-10075: Oracle Content Server – Cross-Site Scripting
漏洞标题 CVE-2017-10075: Oracle Content Server - Cross-Site Scripting 漏洞描述 Oracle Content Server version 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0 are susceptible to cross-site scr...
2017年10月24日 06:09CVE-2021-37292: KevinLAB BEMS (Building Energy Management System) – Backdoor Account
漏洞标题 CVE-2021-37292: KevinLAB BEMS (Building Energy Management System) - Backdoor Account 漏洞描述 KevinLAB BEMS has an undocumented backdoor account, and these sets of credent...
2021年4月26日 23:03CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation
漏洞标题 CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation 漏洞描述 The InstaWP Connect – 1-click WP Staging & Migration plugin for WordP...
2024年8月2日 10:42CVE-2024-3850: Uniview NVR301-04S2-P4 – Cross-Site Scripting
漏洞标题 CVE-2024-3850: Uniview NVR301-04S2-P4 - Cross-Site Scripting 漏洞描述 Uniview NVR301-04S2-P4 contains a reflected cross-site scripting vulnerability via the PATH of LAPI. ...
2024年4月20日 17:16CVE-2022-34305: Apache Tomcat Examples Web Application – Cross-Site Scripting
漏洞标题 CVE-2022-34305: Apache Tomcat Examples Web Application - Cross-Site Scripting 漏洞描述 Apache Tomcat 8.5.50 to 8.5.81, 9.0.30 to 9.0.64, 10.0.0-M1 to 10.0.22, and 10.1.0-M...
2022年1月19日 07:14CVE-2008-6222: Joomla! ProDesk 1.0/1.2 – Local File Inclusion
漏洞标题 CVE-2008-6222: Joomla! ProDesk 1.0/1.2 - Local File Inclusion 漏洞描述 Joomla! Pro Desk Support Center (com_pro_desk) component 1.0 and 1.2 allows remote attackers to read...
2008年3月29日 15:11Adobe Commerce CVE-2022-24086 远程代码执行漏洞
漏洞标题 Adobe Commerce CVE-2022-24086 远程代码执行漏洞 漏洞描述 Adobe Commerce CVE-2022-24086 远程 PoC代码 暂无
2022年2月25日 01:47
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

