
最新发布第827页

【西湖论剑】激发人才自我演进 护航数字时代安全
熠熠生辉的冠军奖杯,高光聚焦的荣光时刻……,随着最终获胜队伍高高举起冠军奖杯,3月12日,西湖论剑·第五届中国杭州网络安全技能大赛决赛多个奖项花落各家,大赛...
 2022年3月16日 09:18

CVE-2025-58360: GeoServer – XML External Entity Injection
漏洞标题 CVE-2025-58360: GeoServer - XML External Entity Injection 漏洞描述 GeoServer 2.26.0 to 2.26.2 and 2.25.6 contains an XML External Entity (XXE) injection caused by insuffic...
2025年8月13日 23:32
自用信息(资产)收集流程
资产收集 CDN判断以及绕过 因为cdn的存在会影响对真实ip的判断,所以第一步判断有无cdn(如果没有直接进入下一步,这里准备了几招)比较重要: 利用多节点请求的返回情况来判断 在线网站17ce 爱站...
2022年3月10日 23:37CVE-2022-31711: VMware vRealize Log Insight < v8.10.2 - Information Disclosure
漏洞标题 CVE-2022-31711: VMware vRealize Log Insight < v8.10.2 - Information Disclosure 漏洞描述 VMware vRealize Log Insight contains an Information Disclosure Vulnerability. A ...
2022年5月11日 22:15Linux locate命令的使用方法_Linux
这篇文章主要介绍了Linux locate命令的使用方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 01. 命令概述 locat...
2024年4月20日 20:18CVE-2021-40247: Budget and Expense Tracker System SQL注入 – 绕过B&E Tracker登录CVE-2021-40247
漏洞标题 CVE-2021-40247: Budget and Expense Tracker System SQL注入 - 绕过B&E Tracker登录CVE-2021-40247 漏洞描述 B&E Tracker v1.0 存在漏洞在从/expense_budget/dist/js/script....
2021年3月10日 00:07CVE-2024-39887: Apache Superset < 4.0.2 - SQL Injection
漏洞标题 CVE-2024-39887: Apache Superset < 4.0.2 - SQL Injection 漏洞描述 An SQL Injection vulnerability in Apache Superset exists due to improper neutralization of special elem...
2024年10月20日 09:11CVE-2018-19287: WordPress Ninja Forms <3.3.18 - Cross-Site Scripting
漏洞标题 CVE-2018-19287: WordPress Ninja Forms <3.3.18 - Cross-Site Scripting 漏洞描述 WordPress Ninja Forms plugin before 3.3.18 contains a cross-site scripting vulnerability. ...
2018年7月17日 05:17CVE-2023-47873: WordPress WP Child Theme Generator < 1.1.3 - Arbitrary File Upload
漏洞标题 CVE-2023-47873: WordPress WP Child Theme Generator < 1.1.3 - Arbitrary File Upload 漏洞描述 Unrestricted Upload of File with Dangerous Type vulnerability in WEN Solutio...
2023年8月25日 10:11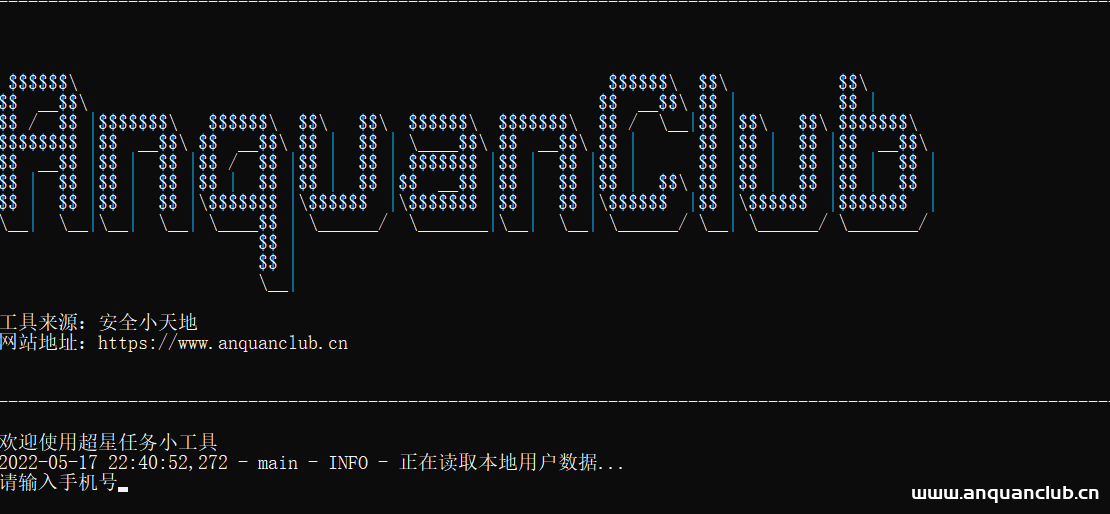
bat脚本案例:实现炫酷的文字logo
需求 我们在日常运行第三方的脚本的时候经常看到非常炫酷的启动logo,比如下图: 不仅美观,而且可以展示品牌和团队标志,提高曝光度。下面详细介绍一下如何用纯batch脚本实现上述效果(powersh...

 2023年3月31日 20:28
CVE-2022-3481: NotificationX Dropshipping < 4.4 - SQL Injection
漏洞标题 CVE-2022-3481: NotificationX Dropshipping < 4.4 - SQL Injection 漏洞描述 The plugin does not properly sanitise and escape a parameter before using it in a SQL statement...
2022年4月21日 17:23CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
2022年10月26日 10:48CVE-2023-35844: Lightdash Arbitrary File Read
漏洞标题 CVE-2023-35844: Lightdash Arbitrary File Read 漏洞描述 Lightdash是一款数据分析平台,它可以让数据团队和其他业务部门聚集在一起以做出更好的数据驱动决策 Lightdash 0.510.3之前...
2023年8月20日 17:37CVE-2023-5074: D-Link D-View 8 v2.0.1.28 – Authentication Bypass
漏洞标题 CVE-2023-5074: D-Link D-View 8 v2.0.1.28 - Authentication Bypass 漏洞描述 Use of a static key to protect a JWT token used in user authentication can allow an for an authen...
2023年2月28日 02:59CVE-2022-0140: WordPress Visual Form Builder <3.0.8 - Information Disclosure
漏洞标题 CVE-2022-0140: WordPress Visual Form Builder <3.0.8 - Information Disclosure 漏洞描述 WordPress Visual Form Builder plugin before 3.0.8 contains a information disclosur...
2022年3月14日 14:34CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting
漏洞标题 CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository hestiacp/hestiacp prior to 1.7.8. PoC代码
2023年6月6日 22:37
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

