
最新发布第878页

CVE-2021-22205: GitLab CE/EE – Remote Code Execution
漏洞标题 CVE-2021-22205: GitLab CE/EE - Remote Code Execution 漏洞描述 GitLab CE/EE starting from 11.9 does not properly validate image files that were passed to a file parser, res...
 2021年11月17日 17:58

自用信息(资产)收集流程
资产收集 CDN判断以及绕过 因为cdn的存在会影响对真实ip的判断,所以第一步判断有无cdn(如果没有直接进入下一步,这里准备了几招)比较重要: 利用多节点请求的返回情况来判断 在线网站17ce 爱站...
2022年3月10日 23:37CVE-2022-2461: Transposh WordPress Translation <= 1.0.8 - Unauthenticated Settings Change
漏洞标题 CVE-2022-2461: Transposh WordPress Translation <= 1.0.8 - Unauthenticated Settings Change 漏洞描述 The Transposh WordPress Translation plugin for WordPress is vulnerabl...
2022年7月28日 13:06CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年4月1日 06:21Apache APISIX 默认密钥漏洞(CVE-2020-13945)
漏洞标题 Apache APISIX 默认密钥漏洞(CVE-2020-13945) 漏洞描述 Apache APISIX是一个高性能API网关。在用户未指定管理员Token或使用了默认配置文件的情况下,ApacheAPISIX将使用默认的管理员...
2020年8月1日 23:23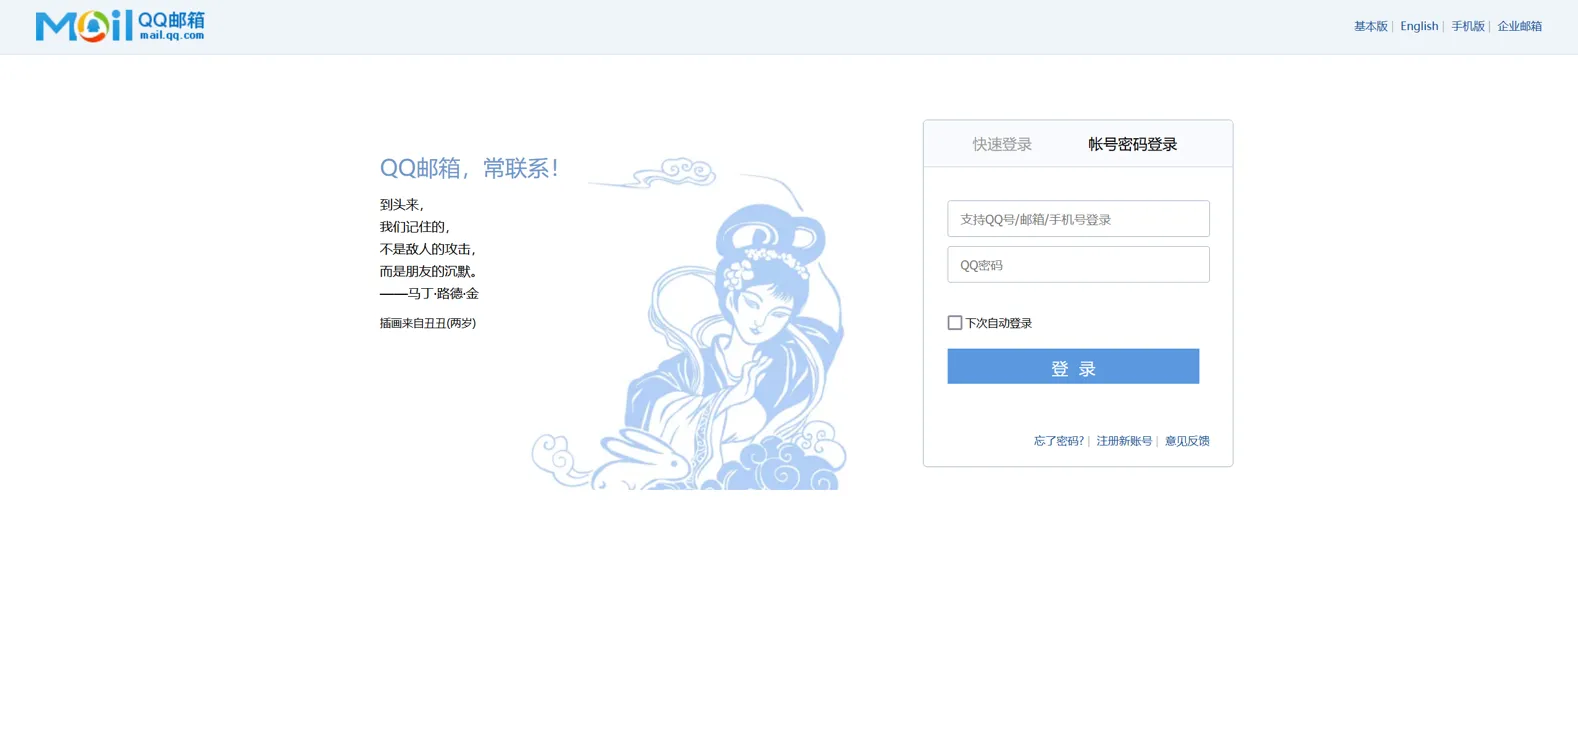
记一次钓鱼网站的渗透记录 ——水文预告!!!
看之前请注意,这是一篇水文,无任何技术!! 记一次钓鱼网站的渗透记录,首先请出我们的主角:114.5x.1xx.xxx 看一下网站打开样子吧 中规中矩的页面,如果你看到这里,认为,这种钓鱼只要一看...

 2023年1月13日 19:37
Atlassian Jira XSS(CVE-2019-3402)
漏洞标题 Atlassian Jira XSS(CVE-2019-3402) 漏洞描述 8.1.1之前的Jira通过searchOwnerUserName参数中的ConfigurePortalPages.jspa资源包含跨站点脚本漏洞。 PoC代码 暂无
2019年10月27日 05:25CVE-2025-25257: Fortinet FortiWeb – SQL Injection
漏洞标题 CVE-2025-25257: Fortinet FortiWeb - SQL Injection 漏洞描述 An improper neutralization of special elements used in an SQL command ('SQL Injection') vulnerability ...
2025年3月20日 03:42
实战小tips (y4师傅传授)
实战小tips (y4师傅传授) 如非php java 写的站如何分辨例如 node.js Flask Django 如果目标机使用了nginx反代 查看js文件 doodoo.js 就是node.js 的框架 查看缓存标识符等等 本文迁移自知识星球...
2022年3月10日 23:34CVE-2019-2588: Oracle Business Intelligence – Path Traversal
漏洞标题 CVE-2019-2588: Oracle Business Intelligence - Path Traversal 漏洞描述 Oracle Business Intelligence versions 11.1.1.9.0, 12.2.1.3.0 and 12.2.1.4.0 are vulnerable to path tr...
2019年12月8日 11:41CVE-2025-30220: GeoServer WFS – XXE Processing Vulnerability
漏洞标题 CVE-2025-30220: GeoServer WFS - XXE Processing Vulnerability 漏洞描述 GeoServer Web Feature Service (WFS) is vulnerable to an XML External Entity (XXE) processing attack d...
2025年4月29日 02:05CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
2022年9月11日 23:59CVE-2017-3132: Fortinet FortiOS < 5.6.0 - Cross-Site Scripting
漏洞标题 CVE-2017-3132: Fortinet FortiOS < 5.6.0 - Cross-Site Scripting 漏洞描述 A Cross-Site Scripting vulnerability in Fortinet FortiOS versions 5.6.0 and earlier allows attac...
2017年10月22日 11:10CVE-2021-25063: WordPress Contact Form 7 Skins <=2.5.0 - Cross-Site Scripting
漏洞标题 CVE-2021-25063: WordPress Contact Form 7 Skins <=2.5.0 - Cross-Site Scripting 漏洞描述 WordPress Contact Form 7 Skins plugin 2.5.0 and prior contains a reflected cross-...
2021年10月8日 21:03CVE-2021-21287: MinIO Browser API – Server-Side Request Forgery
漏洞标题 CVE-2021-21287: MinIO Browser API - Server-Side Request Forgery 漏洞描述 MinIO Browser API before version RELEASE.2021-01-30T00-20-58Z contains a server-side request forge...
2021年2月24日 17:15CVE-2020-21224: Inspur ClusterEngine 4.0 – Remote Code Execution
漏洞标题 CVE-2020-21224: Inspur ClusterEngine 4.0 - Remote Code Execution 漏洞描述 Inspur ClusterEngine V4.0 is suscptible to a remote code execution vulnerability. A remote attack...
2020年11月3日 13:22
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

