
最新发布第879页

CVE-2021-28169: Eclipse Jetty ConcatServlet – Information Disclosure
漏洞标题 CVE-2021-28169: Eclipse Jetty ConcatServlet - Information Disclosure 漏洞描述 Eclipse Jetty through 9.4.40, through 10.0.2, and through 11.0.2 is susceptible to informatio...
 2021年12月6日 08:22
CVE-2024-50340: Symfony Profiler – Remote Access via Injected Arguments
漏洞标题 CVE-2024-50340: Symfony Profiler - Remote Access via Injected Arguments 漏洞描述 symfony/runtime is a module for the Symphony PHP framework which enables decoupling PHP ap...
2024年2月12日 02:33CVE-2024-4325: Gradio – Server-Side Request Forgery
漏洞标题 CVE-2024-4325: Gradio - Server-Side Request Forgery 漏洞描述 A Server-Side Request Forgery (SSRF) vulnerability exists in the gradio-app/gradio version 4.21.0, specificall...
2024年12月18日 23:47CVE-2020-28187: TerraMaster TOS 后台任意文件读取漏洞
漏洞标题 CVE-2020-28187: TerraMaster TOS 后台任意文件读取漏洞 漏洞描述 TerraMaster TOS <= 4.2.06中的多个目录遍历漏洞允许远程身份验证的攻击者通过/tos/index.php?editor/fileGet路径...
2020年9月28日 06:06
bugbounty技巧聚合20220216
漏洞报告 POST URL跳转? 100$ http://hackerone.com/reports/1358977 爆破使用户无法收到2FA验证码导致无法登录 900$ http://hackerone.com/reports/1406495 挖洞技巧 CVE-2022-22536 EXP http...
2022年3月10日 23:29CVE-2023-29204: XWiki – Open Redirect
漏洞标题 CVE-2023-29204: XWiki - Open Redirect 漏洞描述 XWiki Commons are technical libraries common to several other top level XWiki projects. It is possible to bypass the existin...
2023年6月16日 07:17CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
2023年10月12日 11:06CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation
漏洞标题 CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation 漏洞描述 The InstaWP Connect – 1-click WP Staging & Migration plugin for WordP...
2024年8月2日 10:42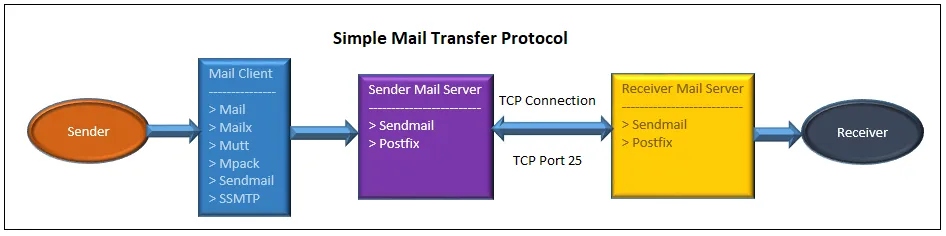
在 Linux 命令行发送邮件的 5 种方法(推荐)_Linux
这篇文章主要介绍了在 Linux 命令行发送邮件的 5 种方法,本教程中包含了最流行的 5 个命令行邮件客户端,你可以选择其中一个,需要的朋友可以参考下 当你需要在 shell 脚本中创建邮件时,就需要...
2026年4月16日 11:45CVE-2011-5252: Orchard ‘ReturnUrl’ Parameter URI – Open Redirect
漏洞标题 CVE-2011-5252: Orchard 'ReturnUrl' Parameter URI - Open Redirect 漏洞描述 Open redirect vulnerability in Users/Account/LogOff in Orchard 1.0.x before 1.0.21, 1.1...
2011年8月20日 22:04CVE-2025-4009: Evertz SDVN 3080ipx-10G – Unauthenticated Arbitrary Command Injection
漏洞标题 CVE-2025-4009: Evertz SDVN 3080ipx-10G - Unauthenticated Arbitrary Command Injection 漏洞描述 The Evertz SDVN 3080ipx-10G is a High Bandwidth Ethernet Switching Fabric for...
2025年1月26日 18:32(CVE-2020-1956) Apache Kylin RESTful API 命令注入漏洞
漏洞标题 (CVE-2020-1956) Apache Kylin RESTful API 命令注入漏洞 漏洞描述 (CVE-2020-1956) Apache Kylin RESTful API 命令注入漏洞 PoC代码 暂无
2020年1月21日 22:59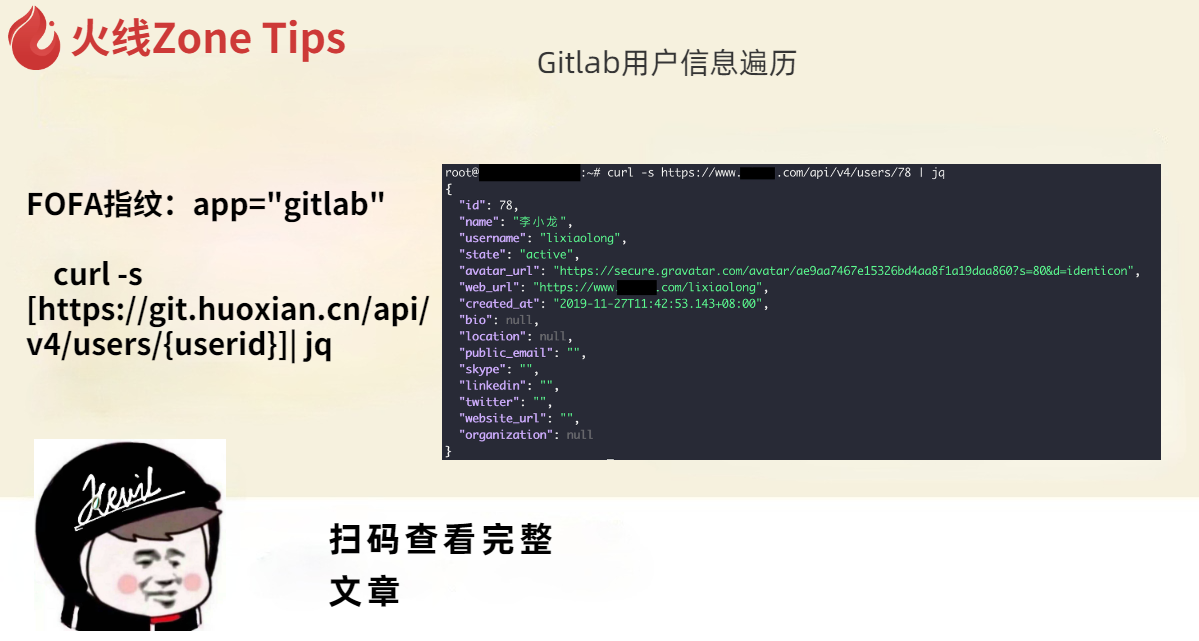
Gitlab用户信息遍历
FOFA指纹:app='gitlab' curl -s http://git.huoxian.cn/api/v4/users/{userid} | jq 文字来源于- 火线 Zone-云安全社区,安全小天地只做文章分享,如有侵权,请联系站长删除
2022年3月10日 23:35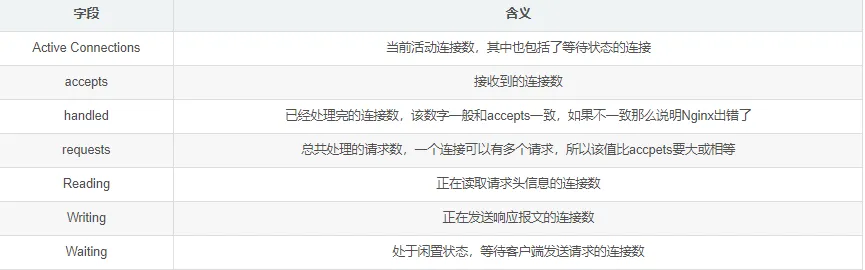
zabbix监控Nginx/Tomcat/MySQL的详细教程_zabbix
这篇文章主要介绍了zabbix监控Nginx/Tomcat/MySQL的详细教程,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 目录zabbix监控Nginxzabbix监控Tomcatzabbix监控MySQLza...
2026年4月19日 11:45CVE-2010-2037: Joomla! Component Percha Downloads Attach 1.1 – Directory Traversal
漏洞标题 CVE-2010-2037: Joomla! Component Percha Downloads Attach 1.1 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the Percha Downloads Attach (com_perchad...
2010年7月5日 22:07CVE-2018-10093: AudioCodes 420HD – Remote Code Execution
漏洞标题 CVE-2018-10093: AudioCodes 420HD - Remote Code Execution 漏洞描述 AudioCodes IP phone 420HD devices using firmware version 2.2.12.126 allow remote code execution. PoC代码
2018年7月12日 13:28
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

