
最新发布第909页

CVE-2020-26413: Gitlab CE/EE 13.4 – 13.6.2 – Information Disclosure
漏洞标题 CVE-2020-26413: Gitlab CE/EE 13.4 - 13.6.2 - Information Disclosure 漏洞描述 GitLab CE and EE 13.4 through 13.6.2 is susceptible to Information disclosure via GraphQL. Use...
 2020年4月30日 20:02
CVE-2014-8676: Simple Online Planning Tool <1.3.2 - Local File Inclusion
漏洞标题 CVE-2014-8676: Simple Online Planning Tool <1.3.2 - Local File Inclusion 漏洞描述 SOPlanning <1.32 contain a directory traversal in the file_get_contents function vi...
2014年11月19日 20:52
腾讯安全发布《2021年移动广告反欺诈白皮书》:2021年广告主因欺诈致损高达220亿
数字技术创新迭代与数字经济蓬勃发展,推动了数字广告的高速增长,与此同时,广告黑灰产也已经形成上下游分工 、配合密切的产业链,逐步蚕食着广告主的预算和对数字广告的信心。近日,由...
2022年4月2日 16:12CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the key and redi...
2025年9月8日 14:30CVE-2023-36346: POS Codekop v2.0 – Cross Site Scripting
漏洞标题 CVE-2023-36346: POS Codekop v2.0 - Cross Site Scripting 漏洞描述 POS Codekop v2.0 was discovered to contain a reflected cross-site scripting (XSS) vulnerability via the nm...
2023年11月20日 06:28CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年6月10日 10:05CVE-2024-29824: Ivanti EPM – Remote Code Execution
漏洞标题 CVE-2024-29824: Ivanti EPM - Remote Code Execution 漏洞描述 An unspecified SQL Injection vulnerability in Core server of Ivanti EPM 2022 SU5 and prior allows an unauthenti...
2024年8月21日 05:44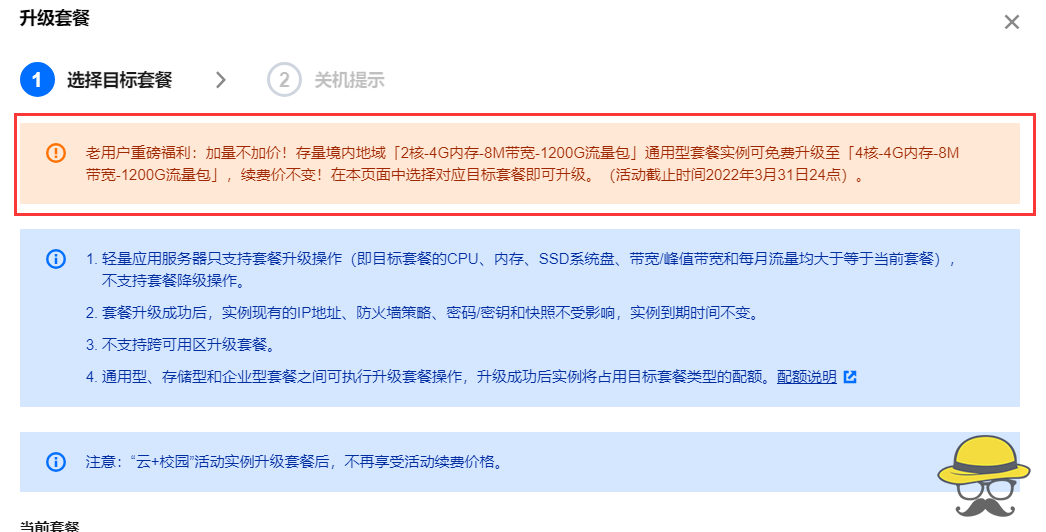
腾讯云老用户重磅福利,通用型套餐实例可免费升级4C4G8M
老用户重磅福利:加量不加价!存量境内地域「2核-4G内存-8M带宽-1200G流量包」通用型套餐实例可免费升级至「4核-4G内存-8M带宽-1200G流量包」,续费价不变!在本页面中选择对应目标套餐即可升级...

 2023年1月13日 20:12
CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting
漏洞标题 CVE-2020-25864: HashiCorp Consul/Consul Enterprise <=1.9.4 - Cross-Site Scripting 漏洞描述 HashiCorp Consul and Consul Enterprise up to version 1.9.4 are vulnerable to ...
2020年8月22日 00:10CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) – Authentication Bypass
漏洞标题 CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) - Authentication Bypass 漏洞描述 Ivanti Endpoint Manager Mobile (EPMM), formerly MobileIron Core, through 11.10 allow...
2023年6月13日 14:14CVE-2021-44228: Apache Log4j2 Remote Code Injection
漏洞标题 CVE-2021-44228: Apache Log4j2 Remote Code Injection 漏洞描述 Apache Log4j2 <=2.14.1 JNDI features used in configuration, log messages, and parameters do not protect aga...
2021年5月19日 13:44CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected)
漏洞标题 CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected) 漏洞描述 The WordPress Qwizcards plugin before version 3.95 does not sanitise and escape th...
2025年11月29日 01:17CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection
漏洞标题 CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection 漏洞描述 The MasterStudy LMS WordPress Plugin for Online Courses and Education plugin for WordP...
2024年6月16日 10:17CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion
漏洞标题 CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion 漏洞描述 Rstudio Shiny Server prior to 1.5.16 is vulnerable to local file inclusion and source code l...
2021年8月9日 09:00Apache ShenYu CVE-2022-23944 信息泄露漏洞
漏洞标题 Apache ShenYu CVE-2022-23944 信息泄露漏洞 漏洞描述 Apache ShenYu CVE-2022-23944 信息泄露漏洞 日期: 2024-02-22 | 影响软件: Apache ShenYu | PoC代码 暂无
2022年9月30日 16:49
匿名者泄露雀巢10GB敏感数据,作为其仍在俄罗斯运营的惩罚
3月22日,匿名者黑客组织在推特账户上发布了瑞士饮品和食品巨头雀巢公司的一份数据库,约有10GB敏感数据泄露,包括公司电子邮件、密码,以及与商业客户相关的数据。同时,匿名者黑客组织还呼吁...
2022年3月27日 14:55
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

