
最新发布第909页

CVE-2022-1713: Drawio <18.0.4 - Server-Side Request Forgery
漏洞标题 CVE-2022-1713: Drawio <18.0.4 - Server-Side Request Forgery 漏洞描述 Drawio prior to 18.0.4 is vulnerable to server-side request forgery. An attacker can make a request...
 2022年10月8日 01:24

Docker+DockerCompose封装web应用的方法步骤_docker
这篇文章会介绍如何将后端、前端和网关通通使用 Docker 容器进行运行,并最终使用 DockerCompose 进行容器编排,感兴趣的可以了解一下 目录技术栈后端构建 api前端构建 web网关构建 gatewayNgin...
2022年6月15日 22:48CVE-2022-25497: Cuppa CMS v1.0 – Local File Inclusion
漏洞标题 CVE-2022-25497: Cuppa CMS v1.0 - Local File Inclusion 漏洞描述 CuppaCMS v1.0 was discovered to contain an arbitrary file read via the copy function. PoC代码
2022年8月14日 23:16CVE-2018-1000226: Cobbler – Authentication Bypass
漏洞标题 CVE-2018-1000226: Cobbler - Authentication Bypass 漏洞描述 Cobbler versions 2.6.11+, but code inspection suggests at least 2.0.0+ and possibly even older versions, may be ...
2018年8月8日 06:54
西迪特 Wi-Fi Web管理系统 未授权RCE漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 西迪特 Wi-Fi Web管理系统 未授权RCE漏洞 西迪特提供的Wireless解决方案为客户提供一套云管理,可靠性高,覆盖范围广的无线组网产品。旨...
2026年2月13日 12:53CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery
漏洞标题 CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery 漏洞描述 WordPress PhonePe Payment Solutions plugin through 1.0.15 is suscept...
2022年7月4日 20:17CVE-2024-4399: WordPress CAS Theme <= 1.0.0 - Server-Side Request Forgery
漏洞标题 CVE-2024-4399: WordPress CAS Theme <= 1.0.0 - Server-Side Request Forgery 漏洞描述 The CAS WordPress theme through version 1.0.0 is vulnerable to Server-Side Request Fo...
2024年10月21日 09:23CVE-2024-37881: SiteGuard WP Plugin <= 1.7.6 - Login Page Disclosure
漏洞标题 CVE-2024-37881: SiteGuard WP Plugin <= 1.7.6 - Login Page Disclosure 漏洞描述 The SiteGuard WP Plugin plugin for WordPress is vulnerable to protection mechanism bypass ...
2024年5月2日 03:54CVE-2021-24285: WordPress Car Seller – Auto Classifieds Script – SQL Injection
漏洞标题 CVE-2021-24285: WordPress Car Seller - Auto Classifieds Script - SQL Injection 漏洞描述 The request_list_request AJAX call of the Car Seller - Auto Classifieds Script Word...
2021年9月7日 11:57CVE-2010-3867: ProFTPD < 1.3.3c - Directory Traversal via mod_site_misc
漏洞标题 CVE-2010-3867: ProFTPD < 1.3.3c - Directory Traversal via mod_site_misc 漏洞描述 ProFTPD versions before 1.3.3c contain directory traversal vulnerabilities in the mod_s...
2010年5月8日 23:27CVE-2022-0218: HTML Email Template Designer < 3.1 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-0218: HTML Email Template Designer < 3.1 - Stored Cross-Site Scripting 漏洞描述 WordPress Email Template Designer WP HTML Mail allows stored cross-site scripti...
2022年5月22日 18:27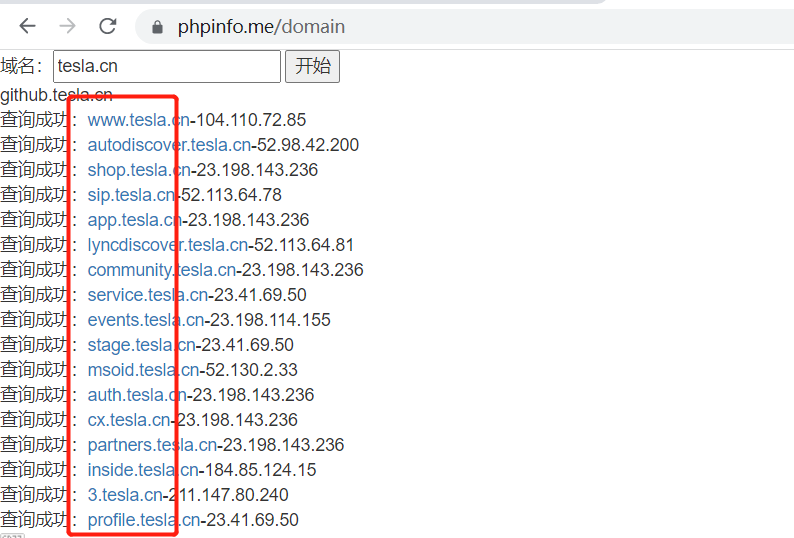
信息收集之“骚”姿势
相信在座的各位都是混迹各大社区论坛很久了 常见的信息收集文章基本上就那些,今天在这里补充一些特别的技巧吧!!!大佬勿喷!!! 0X01字典制作篇 tesla.cn为例子 在线子域名查询 tesla.cn前...
2022年3月10日 23:35CVE-2023-51449: Gradio Hugging Face – Local File Inclusion
漏洞标题 CVE-2023-51449: Gradio Hugging Face - Local File Inclusion 漏洞描述 Gradio LFI when auth is not enabled, affects versions 4.0 - 4.10, also works against Gradio < 3.33 P...
2023年8月17日 03:10CVE-2018-17082: Apache2 – Transfer-Encoding Chunked XSS
漏洞标题 CVE-2018-17082: Apache2 - Transfer-Encoding Chunked XSS 漏洞描述 Apache2 PHP before 5.6.38, 7.0.x before 7.0.32, 7.1.x before 7.1.22, and 7.2.x before 7.2.10 contain a ref...
2018年5月31日 21:40CVE-2021-36748: PrestaHome Blog for PrestaShop <1.7.8 - SQL Injection
漏洞标题 CVE-2021-36748: PrestaHome Blog for PrestaShop <1.7.8 - SQL Injection 漏洞描述 PrestaHome Blog for PrestaShop prior to version 1.7.8 is vulnerable to a SQL injection (b...
2021年11月27日 10:28CVE-2012-1835: WordPress Plugin All-in-One Event Calendar 1.4 – Cross-Site Scripting
漏洞标题 CVE-2012-1835: WordPress Plugin All-in-One Event Calendar 1.4 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in the All-in-One Event Calenda...
2012年8月27日 21:40
2026年11月15日 11:45
2026年11月14日 11:45
2026年11月13日 11:45
2026年11月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

