
最新发布第933页

CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting
漏洞标题 CVE-2016-1000131: WordPress e-search <=1.0 - Cross-Site Scripting 漏洞描述 WordPress e-search 1.0 and before contains a reflected cross-site scripting vulnerability via...
 2016年1月28日 08:32
CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
2022年12月12日 22:09CVE-2022-31499: Nortek Linear eMerge E3-Series <0.32-08f - Remote Command Injection
漏洞标题 CVE-2022-31499: Nortek Linear eMerge E3-Series <0.32-08f - Remote Command Injection 漏洞描述 Nortek Linear eMerge E3-Series devices before 0.32-08f are susceptible to r...
2022年11月28日 05:53CVE-2023-31465: TimeKeeper by FSMLabs – Remote Code Execution
漏洞标题 CVE-2023-31465: TimeKeeper by FSMLabs - Remote Code Execution 漏洞描述 An issue was discovered in FSMLabs TimeKeeper 8.0.17 through 8.0.28. By intercepting requests from v...
2023年2月15日 10:44
深入浅析Centos 7系统的Tomcat服务器_Tomcat
tomcat最初是由Sun的软件架构师詹姆斯 邓肯 戴维森开发的。后来他帮助将其变为开源项目,并由Sun贡献给Apache软件基金会。这篇文章主要介绍了Centos 7系统的Tomcat服务器的相关知识,需要的朋友...
2026年5月15日 11:45CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 – Local File Inclusion
漏洞标题 CVE-2010-1532: Joomla! Component PowerMail Pro 1.5.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the givesight PowerMail Pro (com_powermail) com...
2010年7月12日 15:18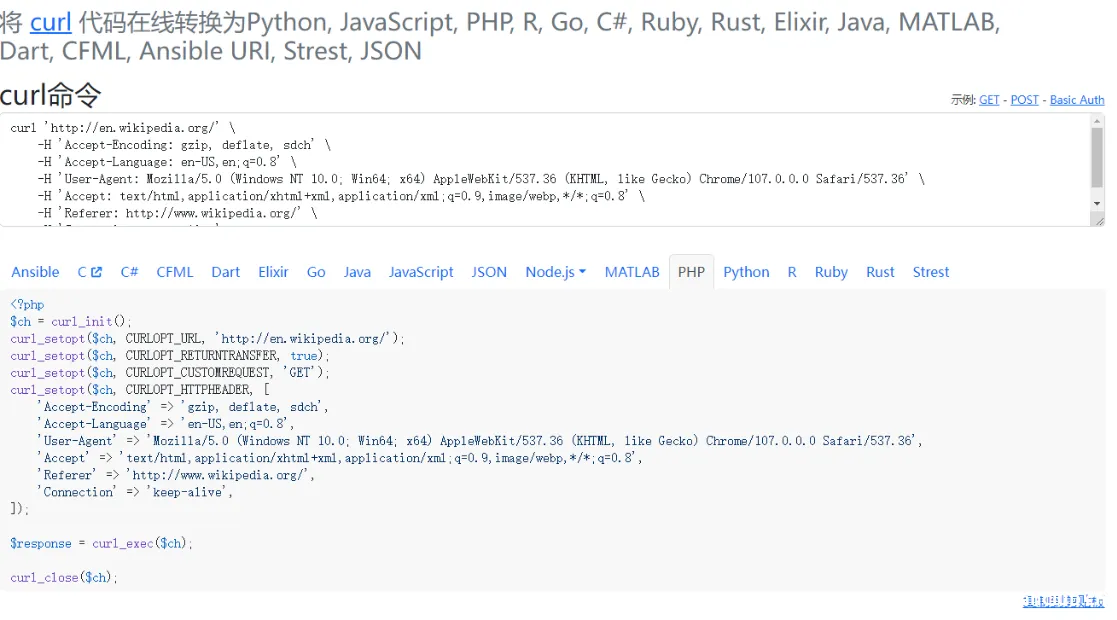
Curl命令在线转换代码工具 | 如何使用工具快速制作脚本
杂谈 最近很多网友表示比较懒,但是curl命令却很香,浏览器里就可以自动获取,然后,有没有什么方式能快速转换成其他格式的代码呢?接下来我们将使用猪猪的新工具Curl命令在线转换工具 在线工具...

 2023年1月13日 19:04
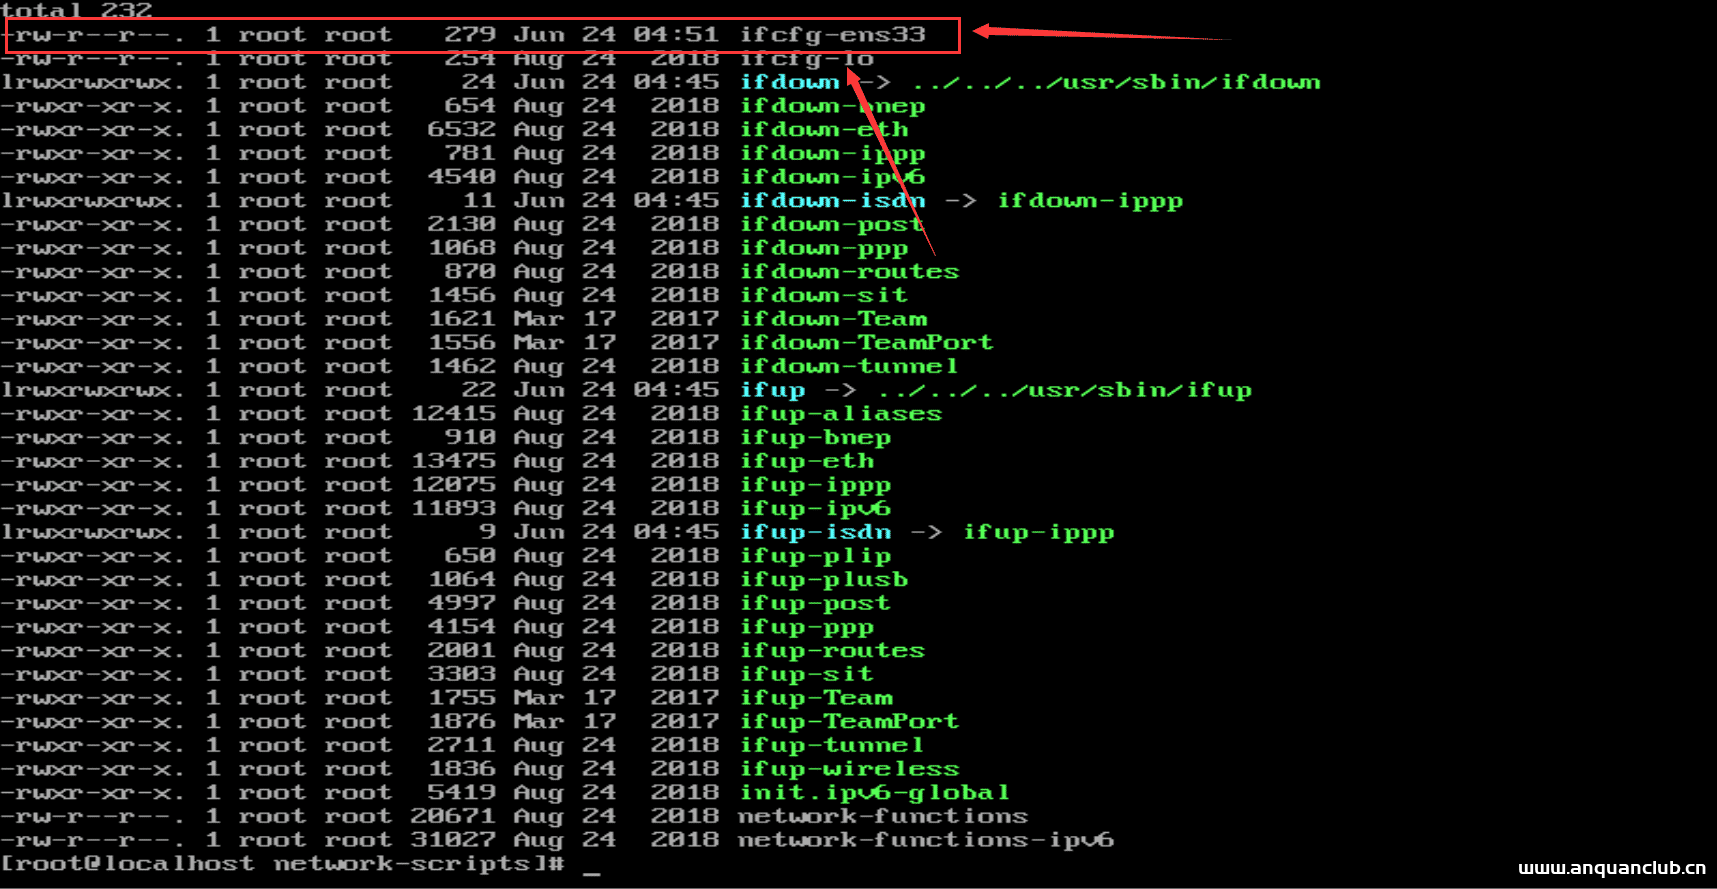
CentOS设置IP连接网络实现过程图解_Tomcat
这篇文章主要介绍了CentOS设置IP连接网络实现过程图解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 1、登录系统,进入:cd /etc/syscon...
2023年4月24日 20:58CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery
漏洞标题 CVE-2022-45835: WordPress PhonePe Payment Solutions <=1.0.15 - Server-Side Request Forgery 漏洞描述 WordPress PhonePe Payment Solutions plugin through 1.0.15 is suscept...
2022年7月4日 20:17CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting
漏洞标题 CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting 漏洞描述 WordPress Download Manager plugin before 2.9.94 contains a cross-site scripting vulne...
2019年7月23日 08:37CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
2018年11月19日 04:41bugbounty技巧聚合20211027
挖洞技巧 What can I do with Open Redirect with OAuth? http://flex0geek.blogspot.com/2021/10/what-can-i-do-with-open-redirect-with.html Metacommunication and Bug Bounty Programs htt...
2022年3月10日 23:39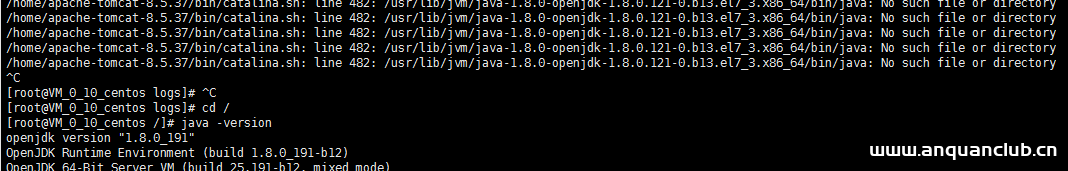
腾讯云服务器tomcat端口无法访问的解决方法_Tomcat
本文主要介绍了腾讯云服务器tomcat端口无法访问的解决方法,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 最近用腾讯云配置了服务器,在使用的时候发现t...
2022年6月15日 22:47CVE-2022-29383: NETGEAR ProSafe SSL VPN firmware – SQL Injection
漏洞标题 CVE-2022-29383: NETGEAR ProSafe SSL VPN firmware - SQL Injection 漏洞描述 NETGEAR ProSafe SSL VPN multiple firmware versions were discovered to contain a SQL injection vul...
2022年10月26日 19:55CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion
漏洞标题 CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion 漏洞描述 WordPress Simple Job Board prior to version 2.9.4 is vulnerable to arbitrary file retr...
2020年7月10日 00:33Casdoor 1.13.0-SQL注入(CVE-2022-24124)
漏洞标题 Casdoor 1.13.0-SQL注入(CVE-2022-24124) 漏洞描述 Casdoor 是一个基于 OAuth 2.0 / OIDC 的 UI 优先集中认证 / 单点登录 (SSO) 平台。该平台存在sql注入漏洞 PoC代码 暂无
2022年2月24日 21:57
2026年10月12日 11:45
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

