
最新发布第952页

CVE-2017-5638: Apache Struts 2 – Remote Command Execution S2-045 S2-046
漏洞标题 CVE-2017-5638: Apache Struts 2 - Remote Command Execution S2-045 S2-046 漏洞描述 Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 is vulnerable to remote comm...
 2017年3月4日 00:23
Apache OFBiz CVE-2023-50968 服务端请求伪造漏洞
漏洞标题 Apache OFBiz CVE-2023-50968 服务端请求伪造漏洞 漏洞描述 Apache OFBiz存在服务器端请求伪造漏洞。此漏洞是由于对requiredLabel参数缺乏校验导致的。 PoC代码 暂无
2023年10月5日 04:34
【溯源小技巧】获取Todesk客户端的手机号与邮箱账号
前言 今天在帮同学使用Todesk远程解决问题的时候,突然想到了以前关于向日葵配置文件的相关利用,可以读取到临时密码,然后使用脚本进行爆破,得到明文之后即可远程连接,现在已经修复了 同理,...

 2024年3月19日 22:36
CVE-2024-28000: WordPress LiteSpeed Cache – Unauthenticated Privilege Escalation to Admin
漏洞标题 CVE-2024-28000: WordPress LiteSpeed Cache - Unauthenticated Privilege Escalation to Admin 漏洞描述 Incorrect Privilege Assignment vulnerability in LiteSpeed Technologies L...
2024年9月16日 18:51CraftCms 代码注入漏洞(CVE-2025-32432)
漏洞标题 CraftCms 代码注入漏洞(CVE-2025-32432) 漏洞描述 攻击者可构造恶意请求利用generate-transform端点触发反序列化,执行任意代码控制服务器,未经身份验证的攻击者可以通过该漏洞在目标...
2025年1月9日 10:31CVE-2017-12794: Django Debug Page – Cross-Site Scripting
漏洞标题 CVE-2017-12794: Django Debug Page - Cross-Site Scripting 漏洞描述 Django 1.10.x before 1.10.8 and 1.11.x before 1.11.5 has HTML autoescaping disabled in a portion of the t...
2017年4月17日 18:18CVE-2020-36510: WordPress 15Zine <3.3.0 - Cross-Site Scripting
漏洞标题 CVE-2020-36510: WordPress 15Zine <3.3.0 - Cross-Site Scripting 漏洞描述 WordPress 15Zine before 3.3.0 is vulnerable to reflected cross-site scripting because the theme ...
2020年10月27日 20:02CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection
漏洞标题 CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection 漏洞描述 Agentejo Cockpit prior to 0.12.0 is vulnerable to NoSQL Injection via the newpassword method of the ...
2020年1月10日 16:35Carel pCOWeb
漏洞标题 Carel pCOWeb <B1.2.4 XSS (CVE-2019-11370) 漏洞描述 B1.2.4之前的Carel pCOWeb易受存储的跨站点脚本攻击,如config/pw_snmp.html“系统联系人”字段所示。 PoC代码 暂无
2019年5月31日 21:08CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure
漏洞标题 CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure 漏洞描述 WordPress EasyCart plugin before 2.0.6 contains an information disclosure vulnerability. An a...
2014年8月7日 13:24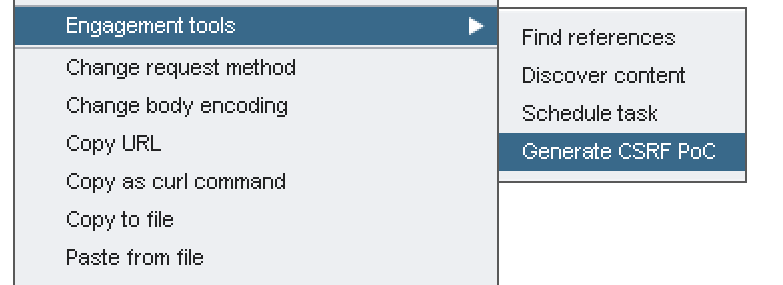
web漏洞挖掘指南 -CSRF跨站请求伪造
web漏洞挖掘指南 CSRF跨站请求伪造 一、CSRF的漏洞原理以及攻击过程 顾名思义,CSRF跨站请求伪造是一种伪造受害者的请求以达成某种目的的攻击手法,本质上我将其理解为攻击者像操控木偶一样让受...
2022年3月10日 23:39CVE-2024-13126: WordPress Download Manager < 3.3.07 - Unauthenticated Data Exposure
漏洞标题 CVE-2024-13126: WordPress Download Manager < 3.3.07 - Unauthenticated Data Exposure 漏洞描述 The WordPress Download Manager plugin before version 3.3.07 does not preven...
2024年10月22日 11:14CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure
漏洞标题 CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure 漏洞描述 TerraMaster NAS devices running TOS prior to version 4.2.30 are vulnerable to informatio...
2022年9月14日 22:12CVE-2013-7285: XStream <1.4.6/1.4.10 - Remote Code Execution
漏洞标题 CVE-2013-7285: XStream <1.4.6/1.4.10 - Remote Code Execution 漏洞描述 Xstream API before 1.4.6 and 1.4.10 is susceptible to remote code execution. If the security frame...
2013年10月11日 02:47CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution
漏洞标题 CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution 漏洞描述 WordPress wsecure plugin before 2.4 is susceptible to remote code execution via shell meta...
2016年5月31日 07:17CVE-2020-2551: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2551: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Oracle WebLogic Server (Oracle Fusion Middleware (component: WLS Core Components) is susceptible to ...
2020年7月30日 22:09
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

