
最新发布第961页

CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection
漏洞标题 CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection 漏洞描述 Prestashop posstaticfooter <= 1.0.0 is vulnerable to SQL Injection via posstaticfooter::...
 2023年6月12日 23:33
CVE-2023-1671: Sophos Web Appliance – Remote Code Execution
漏洞标题 CVE-2023-1671: Sophos Web Appliance - Remote Code Execution 漏洞描述 A pre-auth command injection vulnerability in the warn-proceed handler of Sophos Web Appliance older t...
2023年2月16日 23:52CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting
漏洞标题 CVE-2014-4536: Infusionsoft Gravity Forms Add-on < 1.5.7 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in tests/notAuto_test_ContactServ...
2014年7月8日 21:04CVE-2025-22457: Ivanti Connect Secure – Stack-based Buffer Overflow
漏洞标题 CVE-2025-22457: Ivanti Connect Secure - Stack-based Buffer Overflow 漏洞描述 Ivanti Connect Secure before version 22.7R2.6, Ivanti Policy Secure before version 22.7R1.4, a...
2025年9月16日 11:24Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070)
漏洞标题 Apache OFBiz webtools/control/xmlrpc 远程代码执行漏洞(CVE-2023-49070) 漏洞描述 Apache OFBiz是一个开源的企业资源规划(ERP)系统,提供了多种商业功能和模块。Apache OFBiz 在...
2023年3月14日 03:14CVE-2024-57514: TP-Link Archer A20 v3 Router – Cross-site Scripting
漏洞标题 CVE-2024-57514: TP-Link Archer A20 v3 Router - Cross-site Scripting 漏洞描述 The TP-Link Archer A20 v3 router is vulnerable to Cross-site Scripting (XSS) due to improper h...
2024年6月19日 07:48CVE-2023-4490: WordPress Job Portal < 2.0.6 - SQL Injection
漏洞标题 CVE-2023-4490: WordPress Job Portal < 2.0.6 - SQL Injection 漏洞描述 The WP Job Portal WordPress plugin before 2.0.6 does not sanitise and escape the city parameter bef...
2023年6月8日 14:47
重置Zabbix密码的方法(一步到位)_zabbix
由于长时间不通过账号密码的方式登录zabbix,容易忘记密码,小编今天通过转换对应的md5直接在数据库中重置密码,对重置Zabbix密码感兴趣的朋友一起看看吧 问题描述 由于长期不通过键入账号密码...
2024年5月23日 21:06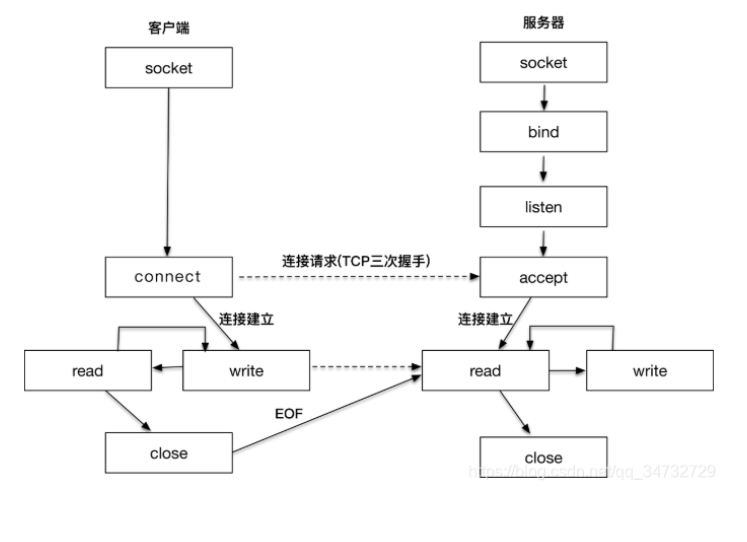
简析Linux网络编程函数_Linux
这篇文章主要介绍了Linux网络编程函数,利用这些基本函数,可以实现tcp协议通讯,可以实现通信。需要了解的小伙伴可以参考一下 目录1,创建套接字socket2,绑定套接字bind3,创建监听;listen4...
2022年6月15日 22:46CVE-2021-27561: YeaLink DM 3.6.0.20 – Remote Command Injection
漏洞标题 CVE-2021-27561: YeaLink DM 3.6.0.20 - Remote Command Injection 漏洞描述 Yealink Device Management (DM) 3.6.0.20 allows command injection as root via the /sm/api/v1/firewal...
2021年7月30日 05:24CVE-2024-57046: Netgear DGN2200 – Improper Authentication
漏洞标题 CVE-2024-57046: Netgear DGN2200 - Improper Authentication 漏洞描述 A vulnerability in the Netgear DGN2200 router with firmware version v1.0.0.46 and earlier permits unauth...
2024年11月28日 10:38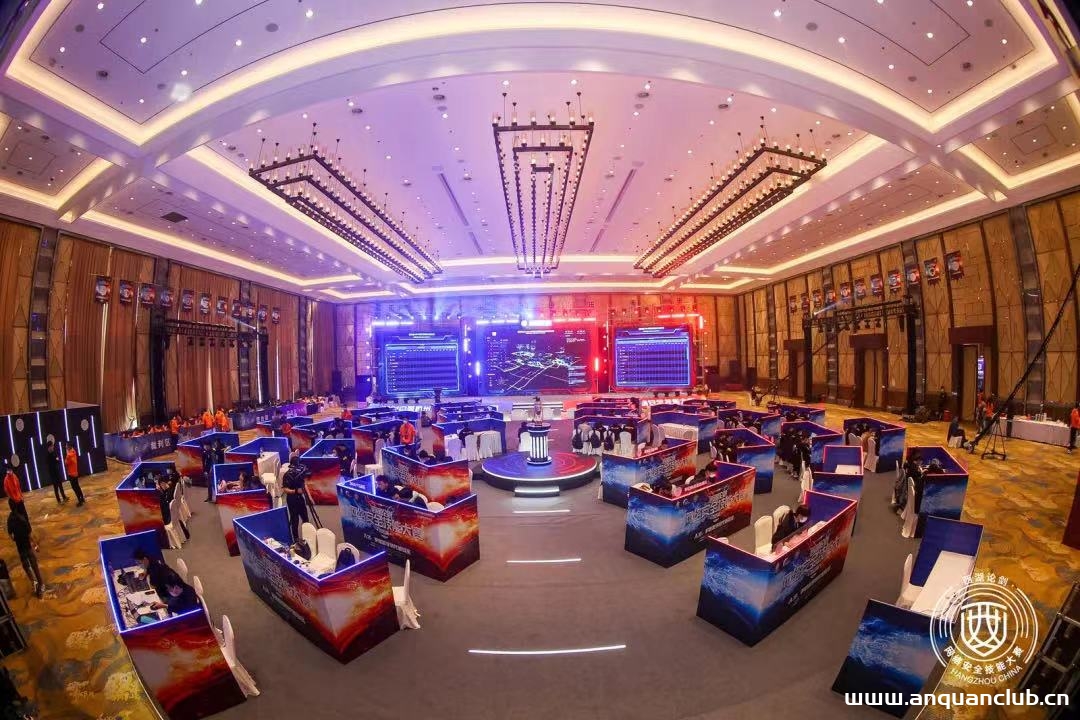
“最强王者”诞生 西湖论剑·第五届中国杭州网络安全技能大赛圆满落幕
随着最终比赛成绩的全部出炉,3月12日下午3点,西湖论剑·第五届中国杭州网络安全技能大赛决赛进入最高潮的颁奖典礼环节,各个奖项尘埃落定,大赛圆满落幕。 当天参加颁奖典礼的领导有杭州...
2022年3月16日 09:16CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 – SQL Injection
漏洞标题 CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 - SQL Injection 漏洞描述 SQL Injection exists in the PrayerCenter 3.0.2 component for Joomla! via the sessionid paramet...
2018年4月24日 22:00CVE-2021-23241: MERCUSYS Mercury X18G 1.0.5 Router – Local File Inclusion
漏洞标题 CVE-2021-23241: MERCUSYS Mercury X18G 1.0.5 Router - Local File Inclusion 漏洞描述 MERCUSYS Mercury X18G 1.0.5 devices are vulnerable to local file inclusion via ../ in co...
2021年12月21日 05:14CVE-2022-0150: WordPress Accessibility Helper <0.6.0.7 - Cross-Site Scripting
漏洞标题 CVE-2022-0150: WordPress Accessibility Helper <0.6.0.7 - Cross-Site Scripting 漏洞描述 WordPress Accessibility Helper plugin before 0.6.0.7 contains a cross-site script...
2022年11月28日 02:37CVE-2020-2883: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2883: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). S...
2020年1月20日 04:28
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

