
最新发布第968页

CVE-2022-25148: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection
漏洞标题 CVE-2022-25148: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection 漏洞描述 The WP Statistics WordPress plugin is vulnerable to SQL Injection due to insufficient ...
 2022年6月21日 06:51
CVE-2021-24220: Multiple Thrive Themes < 2.0.0 - Arbitrary File Upload
漏洞标题 CVE-2021-24220: Multiple Thrive Themes < 2.0.0 - Arbitrary File Upload 漏洞描述 Thrive “Legacy” Rise by Thrive Themes WordPress theme before 2.0.0, Luxe by Thrive The...
2021年12月15日 08:27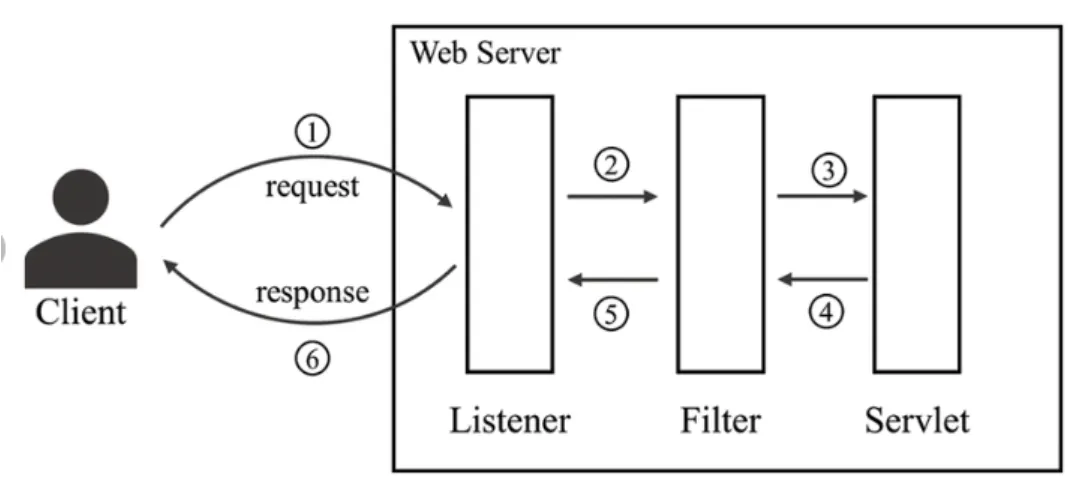
JAVA内存马简介及查杀方法
简介 利用Java Web组件:动态添加恶意组件,如Servlet、Filter、Listener等。在Spring框架下就是Controller、Intercepter。 修改字节码:利用Java的Instrument机制,动态注入Agent,在Java内存...

 2026年3月1日 15:46
CVE-2023-1454: Jeecg Boot QuerySql sql injection
漏洞标题 CVE-2023-1454: Jeecg Boot QuerySql sql injection 漏洞描述 JeecgBoot是一款基于BPM的低代码平台!前后端分离架构 SpringBoot 2.x,SpringCloud,Ant Design&Vue,Mybatis-plus...
2023年8月22日 14:07CVE-2020-8615: WordPress Plugin Tutor LMS 1.5.3 – Cross-Site Request Forgery
漏洞标题 CVE-2020-8615: Wordpress Plugin Tutor LMS 1.5.3 - Cross-Site Request Forgery 漏洞描述 A CSRF vulnerability in the Tutor LMS plugin before 1.5.3 for WordPress can result in...
2020年9月14日 13:18CVE-2018-10822: D-Link Routers – Local File Inclusion
漏洞标题 CVE-2018-10822: D-Link Routers - Local File Inclusion 漏洞描述 D-Link routers DWR-116 through 1.06, DIR-140L through 1.02, DIR-640L through 1.02,DWR-512 through 2.02,DWR-7...
2018年1月17日 13:21
bugbounty技巧聚合20211122
漏洞报告 【Internet Bug Bounty 1,200刀】Ruby - Regular Expression Denial of Service Vulnerability of Date Parsing Methods http://hackerone.com/reports/1404789 【Internet Bug Bounty...
2022年3月10日 23:33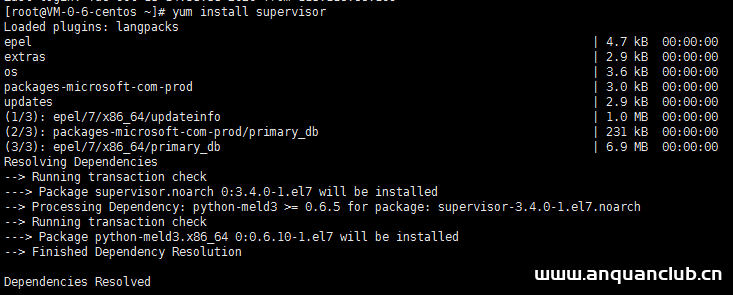
centos7下安装并配置supervisor守护程序的操作方法_Linux
这篇文章主要介绍了centos7下安装并配置supervisor守护程序的操作方法,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 新手,...
2023年4月12日 21:09CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年7月28日 03:59CVE-2021-44910: SpringBlade – Information Leakage
漏洞标题 CVE-2021-44910: SpringBlade - Information Leakage 漏洞描述 SpringBlade is a comprehensive project upgraded and optimized from a commercial-grade project, featuring both a ...
2021年11月4日 14:51CVE-2023-2437: UserPro <= 5.1.1 - Authentication Bypass
漏洞标题 CVE-2023-2437: UserPro <= 5.1.1 - Authentication Bypass 漏洞描述 The UserPro plugin for WordPress through 5.1.1 allows authentication bypass via the userpro_fbconnect A...
2023年1月10日 23:37CVE-2021-25299: Nagios XI 5.7.5 – Cross-Site Scripting
漏洞标题 CVE-2021-25299: Nagios XI 5.7.5 - Cross-Site Scripting 漏洞描述 Nagios XI 5.7.5 contains a cross-site scripting vulnerability in the file /usr/local/nagiosxi/html/admin/ss...
2021年2月15日 23:35CVE-2022-32770: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32770: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
2022年7月18日 08:17CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
2024年4月6日 07:07
命令执行后利用之WebShell文件落地
前言 相信对于命令执行大家都是比较熟悉的吧,输入命令ipconfig、calc、systeminfo、whoami等等 在测试的过程中只要执行这些命令就可以了,但在某些时候,咱们为了进行深入的渗透测试,往往会直...
2024年3月1日 21:52CVE-2021-24316: WordPress Mediumish Theme <=1.0.47 - Cross-Site Scripting
漏洞标题 CVE-2021-24316: WordPress Mediumish Theme <=1.0.47 - Cross-Site Scripting 漏洞描述 WordPress Mediumish theme 1.0.47 and prior contains an unauthenticated reflected cros...
2021年9月20日 16:06
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
2026年10月27日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

