
最新发布第983页

CVE-2023-34928: H3C Magic B1STV100R012 RCE
漏洞标题 CVE-2023-34928: H3C Magic B1STV100R012 RCE 漏洞描述 H3C Magic 是中国新华三(H3C)公司的一款无线路由器。 H3C Magic B1STV100R012版本存在安全漏洞。攻击者利用该漏洞可以进行命...
 2023年10月15日 11:16

Nginx服务器添加Systemd自定义服务过程解析_nginx
这篇文章主要介绍了Nginx服务器添加Systemd自定义服务过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、以nginx为例 使用yum命...
2023年1月19日 20:36
抓捕千人、拦截2700万美元,国际合作打击金融犯罪
与网络诈骗是一种相对低级的犯罪行为的普遍观念相反,实际上诈骗的成功率与涉案金额从来都不低。11月26日,国际刑警组织(已有195个成员国)在其官网上公布了最近一次行动的成果——在代号为HAE...
2022年3月10日 23:38CVE-2001-0537: Cisco IOS HTTP Configuration – Authentication Bypass
漏洞标题 CVE-2001-0537: Cisco IOS HTTP Configuration - Authentication Bypass 漏洞描述 HTTP server for Cisco IOS 11.3 to 12.2 allows attackers to bypass authentication and execute a...
2001年3月3日 11:20
[BJDCTF2020]Easy MD5 – buu刷题笔记
打开连接,只有一个输入框,测试了半天sql,并没有什么鸟用 使用burp抓包,查看报文头发现有信息隐藏在hint里面 select * from 'admin' where password=md5($pass,true) md5($pass,true)知识补...

 2022年4月18日 11:02
CVE-2024-28995: SolarWinds Serv-U – Directory Traversal
漏洞标题 CVE-2024-28995: SolarWinds Serv-U - Directory Traversal 漏洞描述 SolarWinds Serv-U was susceptible to a directory transversal vulnerability that would allow access to read...
2024年11月14日 20:10CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年2月3日 10:21CVE-2019-16469: Adobe Experience Manager – Expression Language Injection
漏洞标题 CVE-2019-16469: Adobe Experience Manager - Expression Language Injection 漏洞描述 Adobe Experience Manager versions 6.5, 6.4, 6.3, 6.2, 6.1, and 6.0 has an expression lang...
2019年4月24日 05:54CVE-2018-14933: NUUO NVRmini – Remote Command Execution
漏洞标题 CVE-2018-14933: NUUO NVRmini - Remote Command Execution 漏洞描述 NUUO NVRmini is vulnerable to unauthenticated remote command execution through the upgrade_handle.php file...
2018年4月3日 14:33CVE-2018-18809: TIBCO JasperReports Library – Directory Traversal
漏洞标题 CVE-2018-18809: TIBCO JasperReports Library - Directory Traversal 漏洞描述 The default server implementation of TIBCO Software Inc.'s TIBCO JasperReports Library, TIB...
2018年1月24日 17:25CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059
漏洞标题 CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059 漏洞描述 Apache Struts 2.0.0 to 2.5.20 forced double OGNL evaluation when evaluated on raw user inp...
2019年5月1日 09:55CVE-2022-23347: BigAnt Server v5.6.06 – Local File Inclusion
漏洞标题 CVE-2022-23347: BigAnt Server v5.6.06 - Local File Inclusion 漏洞描述 BigAnt Server v5.6.06 is vulnerable to local file inclusion. PoC代码
2022年10月18日 13:46
intellij idea 使用Tomcat部署的项目位置在哪_Tomcat
intellij idea 使用Tomcat部署的项目在哪里,为什么不在Tomcat的webapps目录下面,本文通过图文实例相结合给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友参考下吧...
2022年10月8日 21:20CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年12月22日 17:11Apache OFBiz CVE-2018-8033 XML外部实体注入漏洞
漏洞标题 Apache OFBiz CVE-2018-8033 XML外部实体注入漏洞 漏洞描述 Apache OFBiz存在XML外部实体注入漏洞,此漏洞是由于httpService接口对用户的请求验证不当导致的。 PoC代码 暂无
2018年6月5日 07:25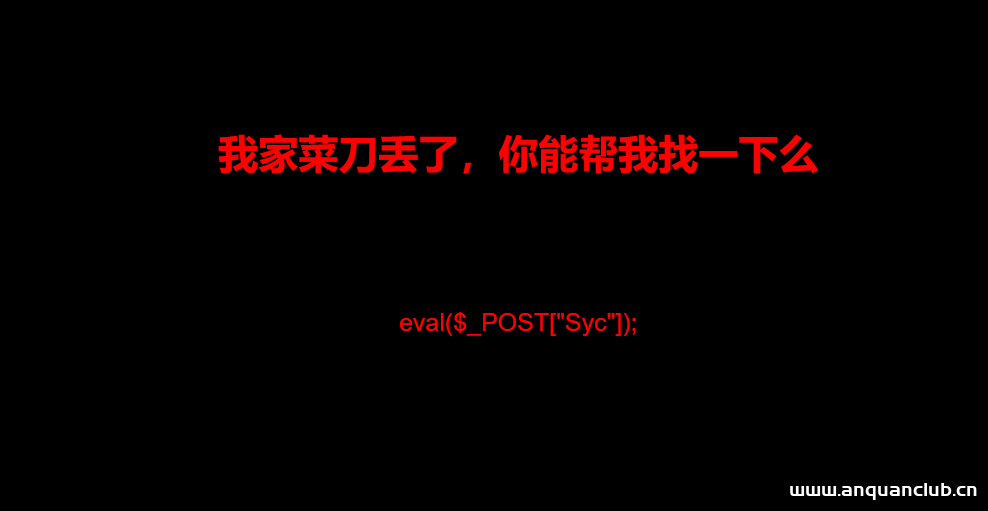
[极客大挑战 2019]Knife – buu刷题笔记
我家菜刀丢了,你能帮我找一下么 一句话木马也在这eval($_POST['Syc']); 现在的问题是木马有了,不知道文件名和路径,尝试目录扫描之后,居然只有一个index.php 按照ctf的尿性,玩的就是脑回路...
2022年4月14日 15:47
2026年10月30日 11:45
2026年10月29日 11:46
2026年10月28日 11:45
2026年10月27日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

