
最新发布第983页

Apache Druid 远程代码执行 (CVE-2021-25646)
漏洞标题 Apache Druid 远程代码执行 (CVE-2021-25646) 漏洞描述 Apache Druid 包括执行用户提供的 JavaScript 的功能嵌入在各种类型请求中的代码。此功能在用于高信任度环境中,默认已被禁用。...
 2021年4月17日 18:13
(2)docker安装教程
前言 通过上一篇文章,我们建议了解了一下,为什么使用容器,接下来我们学习一下docker的安装 安装教程 首先我们进入docker官方安装文档:http://docs.docker.com/ 我们这里选择安装在centos7的...

 2023年2月13日 14:18
Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
2020年8月18日 18:06CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 – Local File Inclusion
漏洞标题 CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in jphone.php in the JPhone (com_jphone) component ...
2010年8月4日 06:57CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability
漏洞标题 CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability 漏洞描述 WordPress Simple Ajax Chat before 20220216 is vulnerable ...
2022年6月5日 18:19CVE-2022-0735: GitLab CE/EE – Information Disclosure
漏洞标题 CVE-2022-0735: GitLab CE/EE - Information Disclosure 漏洞描述 GitLab CE/EE is susceptible to information disclosure. An attacker can access runner registration tokens usin...
2022年1月26日 02:20CVE-2019-3396: Atlassian Confluence Server – Path Traversal
漏洞标题 CVE-2019-3396: Atlassian Confluence Server - Path Traversal 漏洞描述 The Widget Connector macro in Atlassian Confluence Server before version 6.6.12 (the fixed version for...
2019年8月31日 14:38CVE-2023-41763: Skype for Business 2019 (SfB) – Blind Server-side Request Forgery
漏洞标题 CVE-2023-41763: Skype for Business 2019 (SfB) - Blind Server-side Request Forgery 漏洞描述 Skype Pre-Auth Server-side Request Forgery (SSRF) vulnerability PoC代码
2023年9月20日 16:28CVE-2015-1000005: WordPress Candidate Application Form <= 1.3 - Local File Inclusion
漏洞标题 CVE-2015-1000005: WordPress Candidate Application Form <= 1.3 - Local File Inclusion 漏洞描述 WordPress Candidate Application Form <= 1.3 is susceptible to arbitrary...
2015年12月26日 04:36CVE-2021-36580: IceWarp Mail Server – Open Redirect
漏洞标题 CVE-2021-36580: IceWarp Mail Server - Open Redirect 漏洞描述 IceWarp Mail Server contains an open redirect via the referer parameter. This can lead to phishing attacks or ...
2021年10月31日 09:52CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting
漏洞标题 CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting 漏洞描述 The Product Addons & Fields for WooCommerce WordPress ...
2023年9月10日 03:45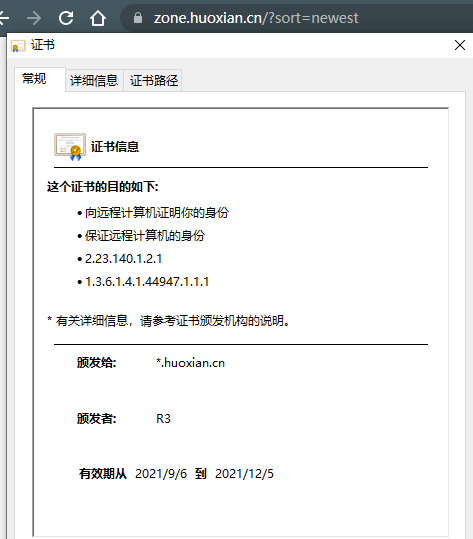
批量获取网站SSL证书里的域名
大佬们在日常刷洞过程中,或者批量扫某个POC时,总会扫到很多未知资产或者结果量太大一个个去验证资产归属太费时费力。而一些https站点的证书中能看到证书归属,一般通过证书定位的资产都比较准...
2022年3月10日 23:33Atlassian Confluence OGNL注入漏洞(CVE-2022-26134)
漏洞标题 Atlassian Confluence OGNL注入漏洞(CVE-2022-26134) 漏洞描述 Atlassian Confluence OGNL注入漏洞(CVE-2022-26134) PoC代码 暂无
2022年4月8日 10:28CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass
漏洞标题 CVE-2024-50477: WordPress Stacks Mobile App Builder <=5.2.3 - Authentication Bypass 漏洞描述 Stacks Mobile App Builder WordPress plugin ≤ 5.2.3 suffers from an authent...
2024年9月10日 02:43CVE-2023-37999: HT Mega – Absolute Addons for Elementor <= 2.2.0 - Missing Authorization to Privilege Escalation
漏洞标题 CVE-2023-37999: HT Mega – Absolute Addons for Elementor <= 2.2.0 - Missing Authorization to Privilege Escalation 漏洞描述 The HT Mega plugin for WordPress is vulnerabl...
2023年6月9日 02:32CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
2023年6月13日 06:50
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

