
最新发布第991页

docker中使用mysql数据库实现局域网访问_docker
在本篇内容里小编给大家整理了关于docker中使用mysql数据库实现局域网访问相关内容,有需要的朋友们可以学习下。 1.获取mysql镜像 docker pull mysql:5.6 注意:此处之所以获取mysql5.6是因为my...
 2024年3月8日 20:40
clash最新RCE复现
杂谈 Clash相信你们都不陌生,就是我们平常使用VPN时最常用的软件 先前就曾出现过rce漏洞,现在有爆出了,可以参考以前的文章 软件版本 0.20.12 操作系统 Windows x64 系统版本 Windows 11 问题...

 2023年1月15日 13:49

CVE-2017-3133: Fortinet FortiOS < 5.6.0 - Cross-Site Scripting
漏洞标题 CVE-2017-3133: Fortinet FortiOS < 5.6.0 - Cross-Site Scripting 漏洞描述 A Cross-Site Scripting vulnerability in Fortinet FortiOS versions 5.6.0 and earlier allows attac...
2017年10月17日 11:14CVE-2016-15042: WordPress Frontend File Manager < 4.0 & N-Media Post Frontend < 1.1 - Arbitrary File Upload
漏洞标题 CVE-2016-15042: WordPress Frontend File Manager < 4.0 & N-Media Post Frontend < 1.1 - Arbitrary File Upload 漏洞描述 The Frontend File Manager plugin (<4.0) a...
2016年3月12日 21:48CVE-2017-7504: JBoss 4.x JBossMQ JMS 反序列化漏洞
漏洞标题 CVE-2017-7504: JBoss 4.x JBossMQ JMS 反序列化漏洞 漏洞描述 fofa: jbossmq PoC代码
2017年4月25日 21:19CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read
漏洞标题 CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read 漏洞描述 Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser t...
2024年10月7日 23:19
解决docker容器重启之后/etc下某些配置文件被重置的问题_docker
这篇文章主要介绍了解决docker容器重启之后/etc下某些配置文件被重置的问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 1. /etc/hosts, /etc/resolv.conf和/etc/hostnam...
2022年8月6日 20:36CVE-2020-2140: Jenkin Audit Trail <=3.2 - Cross-Site Scripting
漏洞标题 CVE-2020-2140: Jenkin Audit Trail <=3.2 - Cross-Site Scripting 漏洞描述 Jenkins Audit Trail 3.2 and earlier does not escape the error message for the URL Patterns field...
2020年12月11日 15:49CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年2月19日 05:43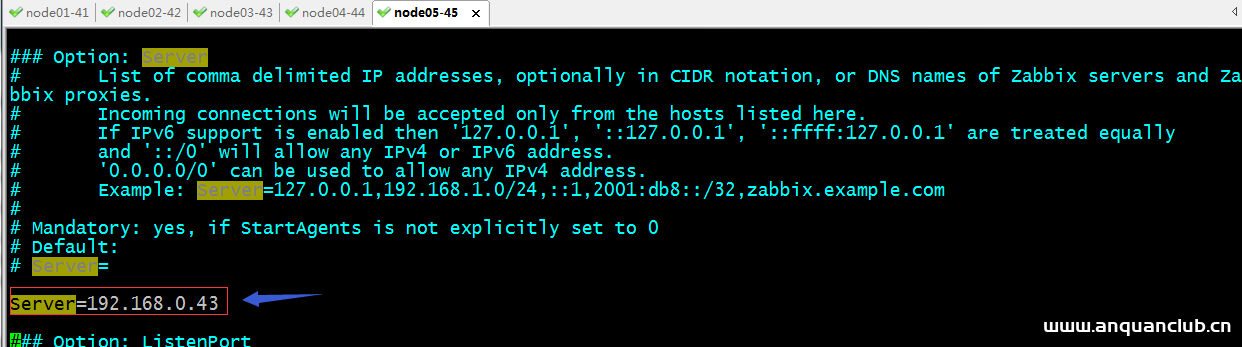
分布式监控系统之Zabbix主动、被动及web监控的过程详解_zabbix
这篇文章主要介绍了分布式监控系统之Zabbix主动、被动及web监控的过程详解,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 前文我们了解了zabbix...
2023年1月9日 20:23CVE-2024-55457: MasterSAM Star Gate v11 – Local File Inclusion
漏洞标题 CVE-2024-55457: MasterSAM Star Gate v11 - Local File Inclusion 漏洞描述 MasterSAM Star Gate v11 is vulnerable to a directory traversal attack via the endpoint /adama/adama...
2024年8月31日 05:09CVE-2025-57808: ESPHome – Authentication Bypass
漏洞标题 CVE-2025-57808: ESPHome - Authentication Bypass 漏洞描述 ESPHome 2025.8.0 contains an authentication bypass caused by improper validation of base64-encoded Authorization v...
2025年4月8日 10:40Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236)
漏洞标题 Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236) 漏洞描述 Adobe Commerce是一款由Adobe公司开发的电子商务平台,广泛应用于全...
2025年1月11日 22:04CVE-2021-42567: Apereo CAS Cross-Site Scripting
漏洞标题 CVE-2021-42567: Apereo CAS Cross-Site Scripting 漏洞描述 Apereo CAS through 6.4.1 allows cross-site scripting via POST requests sent to the REST API endpoints. PoC代码
2021年10月27日 08:18CVE-2023-0527: Online Security Guards Hiring System – Cross-Site Scripting
漏洞标题 CVE-2023-0527: Online Security Guards Hiring System - Cross-Site Scripting 漏洞描述 A vulnerability was found in PHPGurukul Online Security Guards Hiring System 1.0 and cl...
2023年6月11日 03:24CVE-2022-34267: RWS WorldServer – Authentication Bypass
漏洞标题 CVE-2022-34267: RWS WorldServer - Authentication Bypass 漏洞描述 An issue was discovered in RWS WorldServer before 11.7.3. Adding a token parameter with the value of 02 by...
2022年4月4日 02:25
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

