
最新发布第995页

CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting
漏洞标题 CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting 漏洞描述 WordPress WooCommerce before 1.13.22 contains a reflected cross-site scripting vulnerabil...
 2021年8月12日 04:27
CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting
漏洞标题 CVE-2020-17453: WSO2 Carbon Management Console <=5.10 - Cross-Site Scripting 漏洞描述 WSO2 Management Console through 5.10 is susceptible to reflected cross-site script...
2020年10月20日 17:17CVE-2010-1531: Joomla! Component redSHOP 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1531: Joomla! Component redSHOP 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the redSHOP (com_redshop) component 1.0.x for Joomla! a...
2010年5月12日 16:18CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...
2020年11月23日 23:07CVE-2015-2196: WordPress Spider Calendar <=1.4.9 - SQL Injection
漏洞标题 CVE-2015-2196: WordPress Spider Calendar <=1.4.9 - SQL Injection 漏洞描述 WordPress Spider Calendar plugin through 1.4.9 is susceptible to SQL injection. An attacker ca...
2015年5月23日 15:10CVE-2022-1168: WordPress WP JobSearch <1.5.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1168: WordPress WP JobSearch <1.5.1 - Cross-Site Scripting 漏洞描述 WordPress WP JobSearch plugin prior to 1.5.1 contains a cross-site scripting vulnerability....
2022年3月15日 11:54CVE-2023-5561: WordPress Core – Post Author Email Disclosure
漏洞标题 CVE-2023-5561: WordPress Core - Post Author Email Disclosure 漏洞描述 WordPress Core is vulnerable to Sensitive Information Exposure in versions between 4.7.0 and 6.3.1 vi...
2023年6月19日 06:10CVE-2024-29824: Ivanti EPM – Remote Code Execution
漏洞标题 CVE-2024-29824: Ivanti EPM - Remote Code Execution 漏洞描述 An unspecified SQL Injection vulnerability in Core server of Ivanti EPM 2022 SU5 and prior allows an unauthenti...
2024年8月26日 05:56CVE-2021-26086: Atlassian Jira Limited – Local File Inclusion
漏洞标题 CVE-2021-26086: Atlassian Jira Limited - Local File Inclusion 漏洞描述 Affected versions of Atlassian Jira Limited Server and Data Center are vulnerable to local file incl...
2021年6月28日 06:27CVE-2023-27624: WordPress Redirect After Login <= 0.1.9 - Admin Stored XSS
漏洞标题 CVE-2023-27624: WordPress Redirect After Login <= 0.1.9 - Admin Stored XSS 漏洞描述 Marcelotorres Redirect After Login plugin <= 0.1.9 contains a stored cross-site s...
2023年4月2日 20:02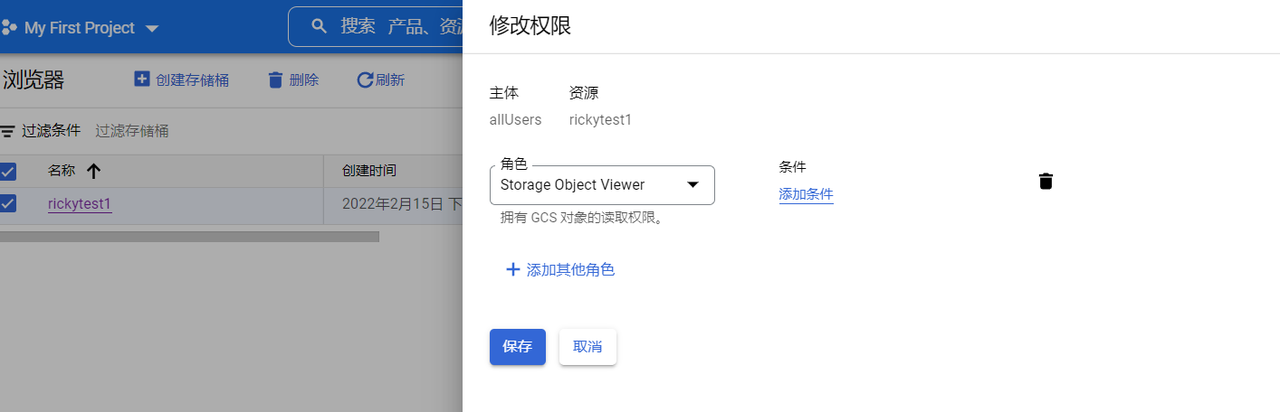
谷歌云 对象存储攻防
本文主要介绍谷歌云对象存储攻防的方式 1、存储桶配置错误-公开访问 当创建的存储桶配置了allUsers拥有GCS对象的读取权限时,该存储桶可以被任何用户公开访问 2、Bucket爆破 当不存在时访问会提...
2022年3月10日 23:38CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection
漏洞标题 CVE-2024-5522: WordPress HTML5 Video Player < 2.5.27 - SQL Injection 漏洞描述 The HTML5 Video Player WordPress plugin before 2.5.27 does not sanitize and escape a param...
2024年12月3日 05:39
tomcat异常解决(Invalid character found in the request target. The valid characters are defined in RFC 7230 and RFC 3986)_Tomcat
这篇文章主要介绍了tomcat 异常的解决方案,帮助大家排查错误,保持服务器的稳定,感兴趣的朋友可以了解下 1.情景展示 tomcat 日志时不时会报出如下异常信息,到底是怎么回事? java.lang.Illeg...
2023年4月2日 20:29CVE-2014-6271: ShellShock – Remote Code Execution
漏洞标题 CVE-2014-6271: ShellShock - Remote Code Execution 漏洞描述 GNU Bash through 4.3 processes trailing strings after function definitions in the values of environment variable...
2014年1月29日 20:34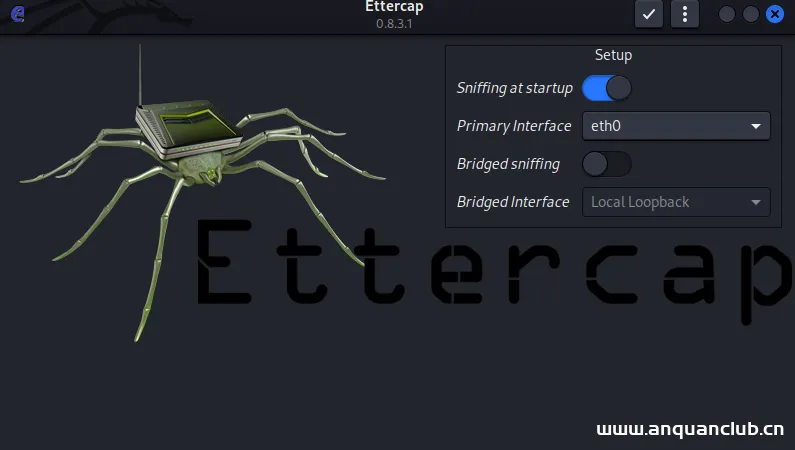
红队钓鱼攻击(2)–DNS劫持&域名劫持介绍及Ettercap实现
前言 文章制作技术分享,请勿用于其他地方,产生的相关责任由使用者负全责。 相关阅读 Ettercap Ettercap是一个综合性的中间人攻击工具,它可以进行ARP欺骗DNS劫持,以欺骗方式的网络嗅探工具,主...

 2026年2月10日 06:54
CVE-2025-54251: Adobe Experience Manager ≤ 6.5.23.0 – XML Injection
漏洞标题 CVE-2025-54251: Adobe Experience Manager ≤ 6.5.23.0 - XML Injection 漏洞描述 Adobe Experience Manager versions 6.5.23.0 and earlier are affected by an XML Injection vulne...
2025年3月3日 20:29
2026年10月23日 11:45
2026年10月22日 11:46
2026年10月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

