
最新发布第524页

CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 – Template Injection
漏洞标题 CVE-2022-29078: Node.js Embedded JavaScript 3.1.6 - Template Injection 漏洞描述 Node.js Embedded JavaScript 3.1.6 is susceptible to server-side template injection via sett...
 2022年3月28日 04:29
CVE-2021-21805: Advantech R-SeeNet 2.4.12 – OS Command Injection
漏洞标题 CVE-2021-21805: Advantech R-SeeNet 2.4.12 - OS Command Injection 漏洞描述 Advantech R-SeeNet 2.4.12 is susceptible to remote OS command execution via the ping.php script f...
2021年6月19日 15:21(CVE-2025-48828) vBulletin模板条件处理任意PHP代码执行漏洞
漏洞标题 (CVE-2025-48828) vBulletin模板条件处理任意PHP代码执行漏洞 漏洞描述 (CVE-2025-48828) vBulletin模板条件处理任意PHP代码执行漏洞 PoC代码 暂无
2025年3月21日 06:35CVE-2010-1354: Joomla! Component VJDEO 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1354: Joomla! Component VJDEO 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the VJDEO (com_vjdeo) component 1.0 and 1.0.1 for Joomla!...
2010年3月20日 00:18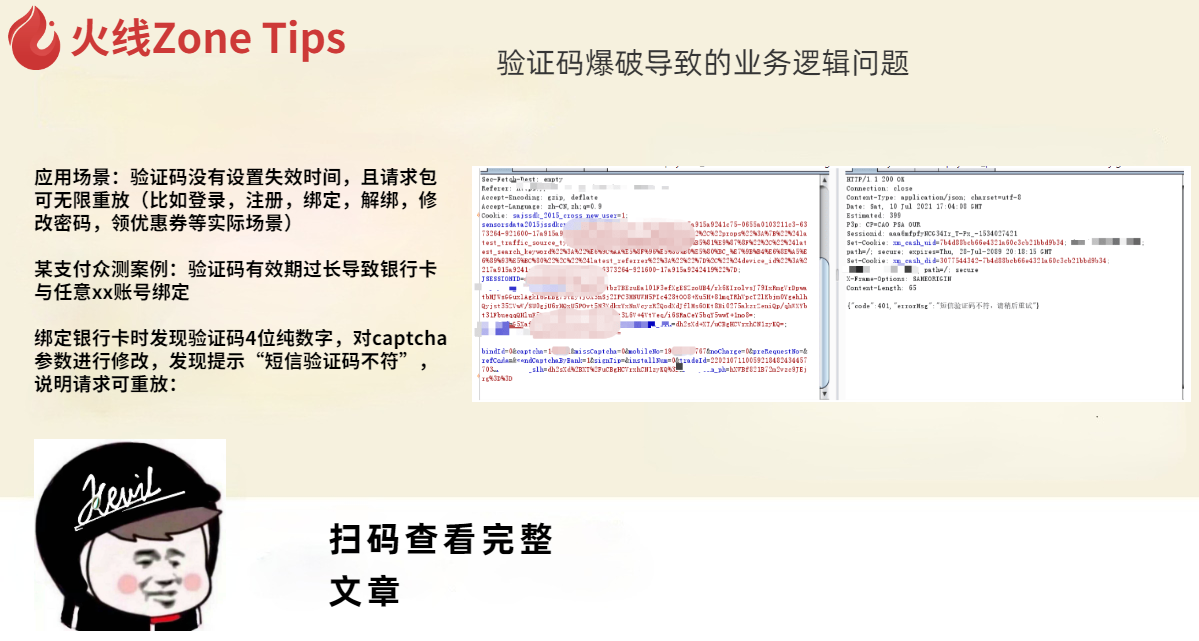
验证码爆破导致的业务逻辑问题
应用场景:验证码没有设置失效时间,且请求包可无限重放(比如登录,注册,绑定,解绑,修改密码,领优惠券等实际场景) 某支付众测案例:验证码有效期过长导致银行卡与任意xx账号绑定 绑定银行...
2022年3月10日 23:37
蓝凌OA treexml.tmpl 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 蓝凌OA treexml.tmpl 远程命令执行漏洞 蓝凌是国内数字化办公专业服务商,阿里钉钉唯一投资的OA厂商,阿里云知识管理与协同领域首家战略合作伙伴。...
2026年2月13日 12:53Apache Druid 任意文件读取(CVE-2021-36749)
漏洞标题 Apache Druid 任意文件读取(CVE-2021-36749) 漏洞描述 在 Druid 摄取系统中,InputSource 用于从某个数据源读取数据。HTTP InputSource 允许经过身份验证的用户以 Druid服务器进程的权...
2021年5月10日 22:17CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
2025年10月26日 21:42CVE-2023-43373: Hoteldruid v3.0.5 – SQL Injection
漏洞标题 CVE-2023-43373: Hoteldruid v3.0.5 - SQL Injection 漏洞描述 Hoteldruid v3.0.5 was discovered to contain a SQL injection vulnerability via the n_utente_agg parameter at /hot...
2023年5月10日 15:54CVE-2024-25608: Liferay Portal – Open Redirect
漏洞标题 CVE-2024-25608: Liferay Portal - Open Redirect 漏洞描述 HtmlUtil.escapeRedirect in Liferay Portal 7.2.0 through 7.4.3.18, and older unsupported versions, and Liferay DXP 7...
2024年6月28日 20:12
空白页面第二种利用
这个页面也是src的,简单打个码,刚开始访问是这个样子滴 我记得我上一篇文章说了xray联动,那这篇就不说了,简单的探测一下,比如nmap,发现这个只有22跟80开放 那没办法,跑一手目录看看,看...
2022年3月10日 23:30CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年8月28日 13:33
docker 容器自定义 hosts 网络访问操作_docker
这篇文章主要介绍了docker 容器自定义 hosts 网络访问操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 在 docker-compose.yml 中增加 extra_hosts 关键字就可以将数据写...
2022年8月6日 20:34CVE-2022-34305: Apache Tomcat Examples Web Application – Cross-Site Scripting
漏洞标题 CVE-2022-34305: Apache Tomcat Examples Web Application - Cross-Site Scripting 漏洞描述 Apache Tomcat 8.5.50 to 8.5.81, 9.0.30 to 9.0.64, 10.0.0-M1 to 10.0.22, and 10.1.0-M...
2022年4月24日 05:15CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload
漏洞标题 CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload 漏洞描述 WordPress SP Project & Document Manager plugin before 4.22 i...
2021年7月8日 21:39CVE-2022-45805: WordPress Paytm Payment Gateway <=2.7.3 - SQL Injection
漏洞标题 CVE-2022-45805: WordPress Paytm Payment Gateway <=2.7.3 - SQL Injection 漏洞描述 WordPress Paytm Payment Gateway plugin through 2.7.3 contains a SQL injection vulnerabi...
2022年11月24日 17:40
2026年11月17日 11:45
2026年11月16日 11:45
2026年11月15日 11:45
2026年11月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

