
最新发布第43页

CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
 2022年1月16日 01:22
CVE-2020-8209: Citrix XenMobile Server – Local File Inclusion
漏洞标题 CVE-2020-8209: Citrix XenMobile Server - Local File Inclusion 漏洞描述 Citrix XenMobile Server 10.12 before RP2, Citrix XenMobile Server 10.11 before RP4, Citrix XenMobile...
2020年2月12日 00:31CVE-2020-15867: Gogs 0.5.5 – 0.12.2 – Remote Code Execution
漏洞标题 CVE-2020-15867: Gogs 0.5.5 - 0.12.2 - Remote Code Execution 漏洞描述 Gogs 0.5.5 through 0.12.2 is susceptible to authenticated remote code execution via the git hooks func...
2020年8月31日 23:29CVE-2021-25297: Nagios 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25297: Nagios 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command injection...
2021年8月21日 19:21
Tenda W15E企业级路由器 RouterCfm.cfg 密码泄露
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 Tenda W15E企业级路由器 RouterCfm.cfg 密码泄露 腾达W15E路由器外置4根5dBi高增益无线天线,同时还内置独立PA和LNA模块,大大增强无线信...
2026年2月13日 12:53
linux下快速列出局域网中所有主机名(计算机名)的脚本_Linux
这篇文章主要介绍了linux下快速列出局域网中所有主机名(计算机名)的脚本,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 最近有列出局域网中所...
2023年9月1日 20:47Apache Tomcat 远程命令执行(CVE-2025-24813)
漏洞标题 Apache Tomcat 远程命令执行(CVE-2025-24813) 漏洞描述 Apache Tomcat 是一个开源的 Java Servlet 容器,广泛用于运行基于 Java 的 Web 应用程序。该漏洞(CVE-2025-24813)允许远程攻...
2025年11月1日 14:51CVE-2021-39350: FV Flowplayer Video Player WordPress plugin – Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-39350: FV Flowplayer Video Player WordPress plugin - Authenticated Cross-Site Scripting 漏洞描述 The FV Flowplayer Video Player WordPress plugin is vulnerable to ...
2021年12月10日 19:18CVE-2023-36934: MOVEit Transfer – SQL Injection
漏洞标题 CVE-2023-36934: MOVEit Transfer - SQL Injection 漏洞描述 In Progress MOVEit Transfer before 2020.1.11 (12.1.11), 2021.0.9 (13.0.9), 2021.1.7 (13.1.7), 2022.0.7 (14.0.7), 2...
2023年12月21日 00:49
白宫辟谣:美国不会为了援助乌克兰而对俄罗斯发起大规模网络攻击
2月24日,美国全国广播公司NBC(美国历史最久、实力最强的商业广播电视公司)刊载了一则新闻,其称收到知情人士消息,已有进行大规模网络攻击的备选方案呈递给了拜登总统,旨在破坏俄罗斯维持其...
2022年3月10日 23:40CVE-2021-31862: SysAid 20.4.74 – Cross-Site Scripting
漏洞标题 CVE-2021-31862: SysAid 20.4.74 - Cross-Site Scripting 漏洞描述 SysAid 20.4.74 contains a reflected cross-site scripting vulnerability via the KeepAlive.jsp stamp parameter...
2021年11月20日 17:14CVE-2023-3380: WAVLINK WN579X3 – Remote Command Execution
漏洞标题 CVE-2023-3380: WAVLINK WN579X3 - Remote Command Execution 漏洞描述 Remote Command Execution vulnerability in WAVLINK WN579X3 routers via pingIp parameter in /cgi-bin/adm.c...
2023年10月12日 04:18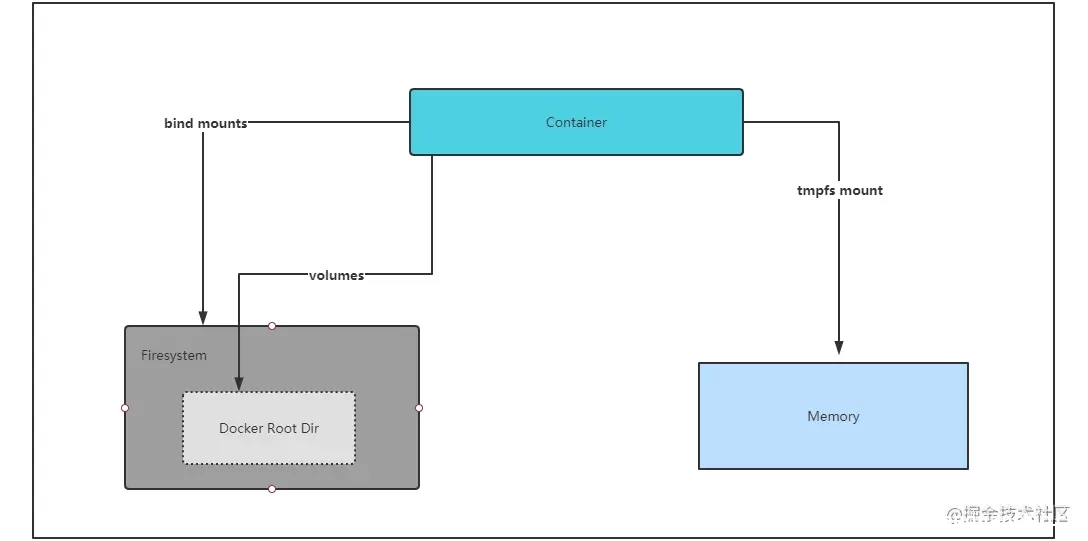
docker容器的几种存储详解_docker
本文主要介绍了docker容器的几种存储方式,主要介绍了3种,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录写在前面几种存储挂载方式1.bind mounts2.v...
2022年6月21日 21:38CVE-2022-31137: Roxy-Wi options.py 远程命令执行漏洞
漏洞标题 CVE-2022-31137: Roxy-Wi options.py 远程命令执行漏洞 漏洞描述 Roxy-Wi options.py 存在远程命令执行漏洞,攻击者通过漏洞可以执行命令获取服务器权限 app="HAProxy-WI" P...
2022年9月5日 22:22CVE-2018-20062: ThinkPHP 5.0.23 – Remote Code Execution
漏洞标题 CVE-2018-20062: ThinkPHP 5.0.23 - Remote Code Execution 漏洞描述 An issue was discovered in NoneCms V1.3. thinkphp/library/think/App.php allows remote attackers to execute...
2018年10月15日 05:49Apache OFBiz RMI反序列化前台命令执行(CVE-2021-26295)
漏洞标题 Apache OFBiz RMI反序列化前台命令执行(CVE-2021-26295) 漏洞描述 OFBiz是基于Java的Web框架,包括实体引擎,服务引擎和基于小部件的UI。近日,Apache OFBiz官方发布安全更新。Apache ...
2021年10月3日 04:58
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

